Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
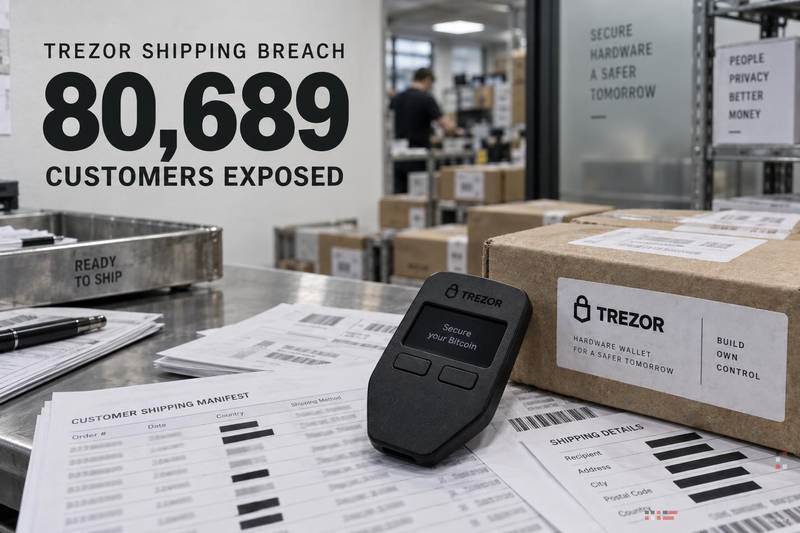
Trezor disclosed data breach incident with third-party logistics providers: 80,689 customer information was affected
Hardware wallet manufacturer Trezor disclosed in its official incident notice that a data breach occurred at one of its logistics service providers, resulting in the exposure of contact and delivery details of 80,689 customers. Trezor emphasized that its own systems, products and equipment had not been compromised.
Summary of Core Points
- Trezor pointed out that the data breach originated from third-party logistics provider ShipMonk.
- Sensitive information such as customer contact information and delivery address was exposed.
- According to Trezor statistics, a total of 80,689 customers were affected.
Accident details and scope
Trezor blamed the incident on a data breach suffered by its compliance and logistics partner ShipMonk, rather than a breach of the company's own infrastructure. According to Trezor's current Frequently Asked Questions (FAQ) for accidents, the total number of customers affected is 80,689.
It is worth noting that the current total number affected is much higher than the data originally disclosed on August 13. The original disclosure at the time included only 11,742 customers with full disclosure and 1,947 customers with partial disclosure, and these data only represent the original group rather than the updated overall statistics.
In an update on September 4, Trezor said that the company learned on September 2 that the leak also involved approximately 67,000 additional U.S. customers, and that the data corresponds to orders placed between November 2019 and August 2021. Despite Trezor's repeated requests and ShipMonk's written assurance that the data had been deleted, these historical records remained.
"We were very disappointed that despite receiving a reply confirming the deletion, the data was not deleted from their system."
-- Trezor Team, Official Incident Update
Trezor explained that its customer order data retention policy is 90 days, which is why records from 2019 to 2021 conflict with the results it expected from suppliers. This is the second data processing incident affecting Trezor customers after previous email provider leaks.
Which customer information was leaked?
Trezor pointed out that the complete leaked dataset included names, email addresses, phone numbers, shipping addresses and order numbers. In addition, the 1,947 partially leaked records only contained names, cities and e-mails, and did not include the shipping address.
Crucially, Trezor emphasizes that its systems, products and services have not been infringed and that the equipment remains secure. This was a breach of contact and order data, not a theft of the wallet private key.
Report what is not confirmed
The disclosure did not indicate that passwords, payment information, private keys or mnemonic words were involved. Trezor said it had notified affected customers directly and advised them not to share wallet backups or enter backup information on the website.
Trezor warned that exposed contact information could lead to phishing emails, fraudulent phone calls or letters, and even pose potential physical security risks. These are risks that have been warned about, not consequences that have been verified for this dataset. Competitor Ledger has recorded similar attacks, including sending physical letters instructing recipients to scan QR codes and enter mnemonic words, but these are separate Ledger incidents and are not related to this Trezor data breach. This pattern echoes long-standing concerns that Trezor hardware users have been targets of phishing.
Similar data breaches have occurred to other competing brands this year, such as the SafePal breach that affected more than 53,000 cryptocurrency holders, highlighting vendor-side data processing as a risk for the entire industry. At the same time, Trezor continues to advance product development and recently launched a Safe 7 hardware wallet that supports quantum security.
What is unclear about the leak
Trezor attributed the commitment to retain and delete records to ShipMonk, but no independent auditor has yet verified the vendor's behavior or the details of the affected customer data set. Therefore, the relevant counting and deletion statements should be regarded as Trezor's unilateral statements.
There have been no confirmed downstream theft, fraud or physical attacks related to such records. The widely circulated analysis claiming "zero economic losses" was not supported by official reports, according to unconfirmed reports. In addition, reports blaming the Metabase vulnerability for the original intrusion have not yet been verified.
At the time of studying snapshots, Bitcoin was trading at US$77,159, down 0.32% in 24 hours; there is currently no evidence that this disclosure is related to price fluctuations.
Follow-up concerns: Further updates to the Trezor FAQ, whether ShipMonk issued a statement, and whether affected customers will report targeted phishing in the next few days.