Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
 ETH
 XRP
硬件钱包篡改疑云蔓延至欧洲,XRP底层漏洞与AI加密风险引发行业关注
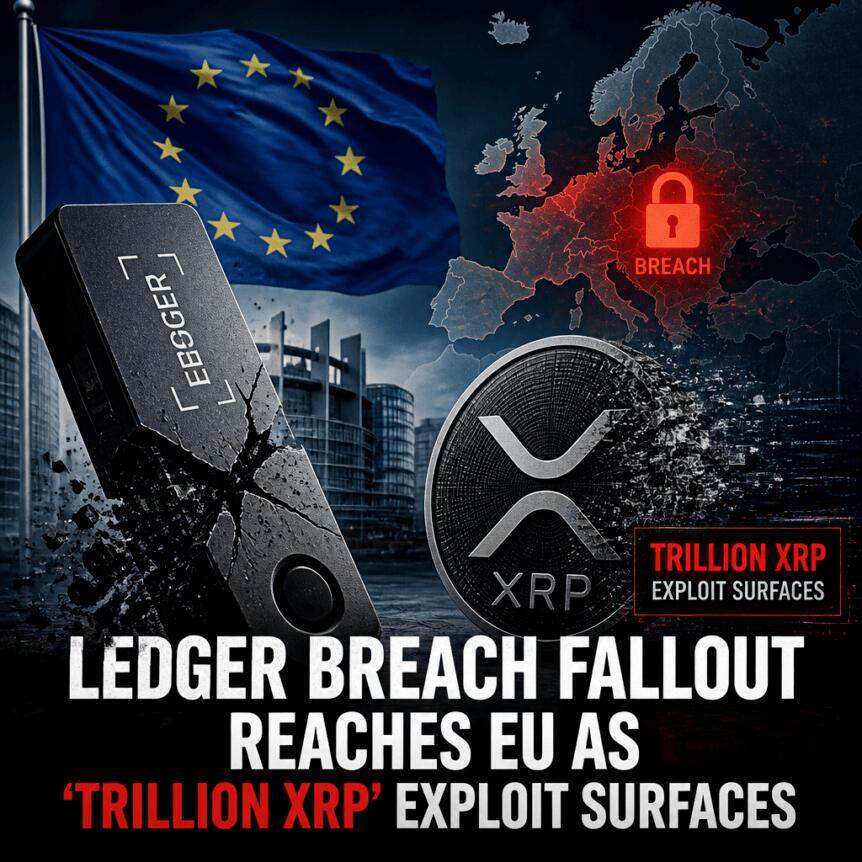
据报道,一款据称与东南亚早期资金损失事件相关的篡改版Ledger硬件钱包出现在欧洲,这引发了人们对受损设备分销范围广泛性的新的质疑。此前,一家网络安全机构估计,该事件已导致亚洲客户约9340万美元的资金被盗。
与此同时,本周加密货币生态系统还迎来了其他与安全相关的更新:包括Veria Labs因修复一个可追溯至2015年的XRP Ledger溢出漏洞而获得25万美元的漏洞赏金;以及以太坊联合创始人Vitalik Buterin针对“AI加速密码学突破”发出的新一轮“地堡模式”(bunker mode)警告。
核心要点
- 欧洲出现改装Ledger设备:新报告称,一台经过修改的Ledger设备在欧洲MediaMarkt商店被购买,但截至目前,尚未有来自该设备的资金被盗报告。
- Ledger未确认关联:Ledger此前曾要求在过去90天内从东南亚经销商CryptoBilis购买设备的客户考虑转移资产,但并未确认欧洲发现的设备属于同一攻击方案的一部分。
- XRP漏洞赏金:Veria Labs因发现并修复XRP代码中的溢出漏洞获得25万美元赏金。该漏洞已被迅速修补,且未被认为遭到利用。
- AI对密码学的威胁:Vitalik Buterin supported researcher Justin Drake and called on the industry to be prepared because AI systems could accelerate mathematical discoveries related to blockchain security.
- Other security incidents: Other ecosystem security incidents mentioned this week include phishing links on Coldcoin's official X account and Tether's alleged temporary freezing of funds associated with the THORChain vault.
The Ledger tampering incident is suspected to extend beyond Asia, but officials have not yet confirmed the full picture.
The core of the Ledger incident is that some devices were implanted with "implants" designed to undermine the restoration of mnemonic access. Previous reports have linked the tampering to specific hardware sold through Asian authorized dealer CryptoBilis because the devices were found to have been modified in some way, allowing attackers to read mnemonic words even if the devices passed an authenticity check on appearance.
According to information provided by a European X user named Johannes, he showed a photo showing he purchased a tampered Ledger device from European consumer electronics retailer MediaMarkt about two weeks ago. Johannes claims that the implant appears to be an early model in a previous version related to damaged Ledger shipments in Asia.
Johannes speculated that the equipment he purchased may be inactive or reserved for subsequent wider launches. He pointed out that either the damaged device failed or the attacker was waiting for a larger-scale promotion. He also emphasized that in the cases he reported, no funds were stolen.
前Mt. Gox首席执行官Mark Karpeles提供了更多背景信息,他指出设备天线上可见的部分是一个“欧亚版本”。其暗示是,由于移动网络频率的差异,可能存在针对不同地区的不同植入物变体。然而,Ledger尚未确认这台欧洲设备属于同一更广泛的攻击链条。
针对东南亚事件,Ledger的反应包括要求CryptoBilis暂停销售和发货作为预防措施。Ledger还建议在过去90天内从CryptoBilis购买设备的客户考虑将资产转移到新的Ledger设备上。Ledger表示受影响设备的数量有限,并通过其官方渠道发布了更新以承认此事。
虽然网络安全媒体Yfarmx估计总损失为9340万美元,涉及471个地址,但该数字尚未得到Ledger的独立确认。加上这份来自欧洲的未经证实关联的报告,意味着投资者和用户应将此事件视为不断演变的风险,而非已结束的区域性事件。
值得关注:真实性检查并非万无一失
早期报道中描述的Ledger妥协事件中,最具决定性的方面之一是,被篡改的设备据报道在允许盗窃的同时,似乎通过了真实性检查。这一细节至关重要,因为它改变了用户对“安全”购买渠道的看法,以及对单一设备验证可靠性的认知。
Ledger在CryptoBilis关联问题后的指导方针——即让特定窗口期内的买家转移资产——旨在降低即使设备没有明显迹象时的暴露风险。如果欧洲的报告最终被证明与同一植入物家族或分销方法有关,它可能会将早期的指导原则的实际影响扩展到东南亚以外。
然而,在此阶段,读者应区分“声称”(在欧洲购买了被篡改的设备)和“已确认”的事实(Ledger尚未验证该欧洲设备与之前与亚洲相关的活动有关)。在Ledger提供确认之前,最安全的解读是风险范围可能在地理上有所扩展,但确切范围仍不确定。
XRP Ledger漏洞赏金:溢出问题已修补,无证据表明遭利用
安全公司Veria Labs宣布,在发现XRP代码中自2015年以来隐藏的一个溢出漏洞后,获得了25万美元的漏洞赏金。Veria Labs声称,如果未及时修补,攻击者可以构建一笔交易,凭空打印出极端数量的XRP。
据Veria Labs称,该漏洞已被修补,且“没有证据”表明它曾被利用。该公司联合创始人Cayden Liao在X上写道,其AI代理审查了运行XRP Ledger的软件(rippled),发现了两个低严重性漏洞。Liao表示,这两个问题可以被串联起来,产生比单个漏洞单独存在时更大的 exploit。
In the description provided by Liao, a single carefully constructed exploit transaction could generate more than 18 trillion XRPs, which would be well above the total supply of the asset. He defines severity as the result of the interaction of vulnerabilities, rather than the isolated behavior of individual issues. Veria Labs also said the vulnerabilities were reported on September 22 and RippleX patched them three days later.
The practical lesson for XRP holders is that quick remediation and reporting of unutilized situations are meaningful guarantees. For the broader market, the incident strengthens the view that "low-severity" vulnerabilities can still become critical when combined accidentally, especially if adversaries test marginal case behavior.
Vitalik Buterin endorses AI's "bunker mode" warning
Ethereum co-founder Vitalik Buterin commented on researcher Justin Drake's warning that AI is accelerating mathematical progress related to blockchain cryptography. Buterin said he does not recommend moving funds immediately, but the industry should "take seriously the cryptographic risks posed by AI-accelerated mathematics."
Drake previously urged ecosystems to prepare for a "bunker model" after OpenAI reportedly released hundreds of new mathematical discoveries that are difficult for humans to solve. Drake's concern is not that cryptography has been cracked, but that AI systems may over time help discover structural weaknesses in elliptic curve cryptography or lattice-based cryptography.
Other projects and analysts criticized the warnings as creating panic, arguing that there is currently no evidence that AI agents are close to cracking cryptography. Still, Buterin's response suggests that Ethereum leadership believes the scenario has sufficient credibility and therefore encourages more proactive research and planning.
Even if there is no imminent threat, this stance is still important to long-term users and developers, because cryptographic migrations are often slow, complex and expensive-even if the timetable remains speculative, early preparation is valuable.
Other security signals mentioned this week
Coldcard phishing incident: Coldcard, a hardware wallet that only supports Bitcoin, said it is investigating an unauthorized phishing link that appeared on its official X account. The post was deleted despite using offline two-factor authentication. The company said its only official website is coldcard.com.
THORChain funds freeze allegations: THORChain technology co-founder Chad Barraford accused Tether of temporarily freezing USDt (USDT) vaults associated with THORChain. Barraford alleges Tether blacklisted specific vault addresses and subsequently lifted the freeze when the transaction resumed.
Former Celsius CEO Ban: New York State permanently bans former Celsius CEO Alex Mashinsky from entering the cryptocurrency, securities and commodities industries. It was part of a settlement with New York Attorney General Letitia James that included conditional payments of up to $35 million. The case stems from allegations that Mashinsky misled hundreds of thousands of investors before the collapse of Celsius.
随着这些故事的发展,读者应关注Ledger关于疑似欧洲设备的原始确认,以及澄清XRP Ledger漏洞是否具有超越已修补问题之外更广泛影响的额外安全建议;同时,随着AI驱动研究的不断进步,“地堡模式”规划仍是行业待解的开放性问题。