Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
Key Facts
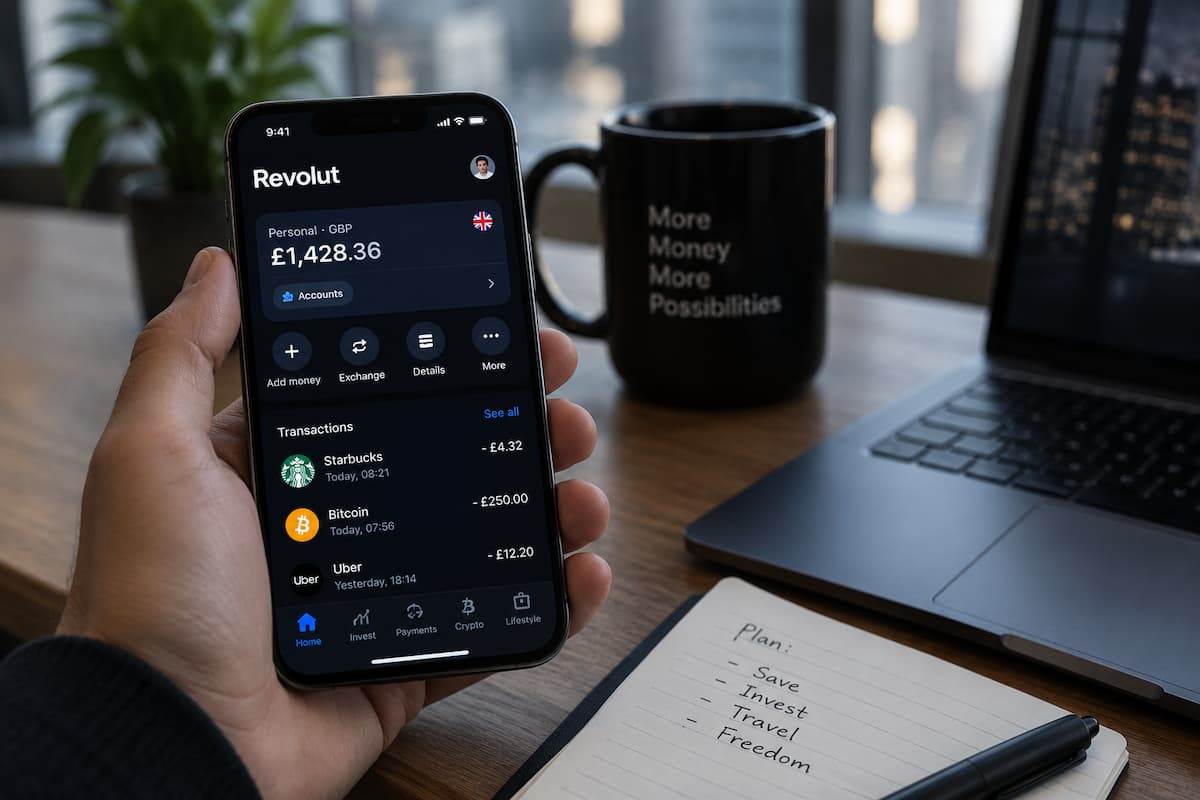
Revolut is suspected of providing true customer records to forged government data requests. According to reports, the leaked data included identification documents associated with the affected accounts and Bitcoin transaction history. As of the time of writing, the company has not issued a public statement specifically addressing this incident.
It is reported that after receiving a false data request posing as a government agency, Revolut handed over the customer's identity documents and Bitcoin transaction records, rather than a request from a real government agency. If this is true, the error falls into a clear and common category: it was not a hacker attack on the Revolut system, but a procedural vulnerability caused by the company's failure to effectively verify the identity of the requester before delivering the data.
Differences between such failure patterns and traditional data breaches
Traditional data breaches mean that attackers break through technical defenses and exploit vulnerabilities in code or infrastructure to extract data. The situation described here is a social engineering failure: the request is carefully packaged, worded as if it came from law enforcement or regulatory agencies, and sent through channels that the company considers legal by default. Financial institutions often have fast processing processes for real government requests because law enforcement sometimes needs to obtain records quickly, a speed that realistic forged documents are designed to exploit. The key to solving such problems lies in procedural measures that independently verify the identity of the requesting organization before responding, rather than technical fixes like software patches.
The specific leaked data content reported is more serious than the general reference to "customer data." Identity documents are the basic material for implementing account takeovers and further identity fraud. Bitcoin transaction histories linked to real identities fall into the rarer and more sensitive category of leaks because they can link specific individuals to wallet activities that may not be expected to be traced back. The risks posed by this exposure go beyond the scope of typical financial fraud and have subsequent knock-on effects.
Confirming key elements of this matter
As of this writing, Revolut has not issued a special statement about this specific incident through its official channels, including the newsroom or the published anti-fraudulent account protection guidelines. For a company as large and heavily regulated as Revolut, the silence itself is noteworthy because once such breaches are confirmed, they often trigger mandatory notification obligations under data protection laws in the jurisdiction in which they operate. Anyone who believes their Revolut account information may be affected can raise concerns directly through the company's cybercrime report catalog, which lists relevant national authorities in each market. Until Revolut or the national data protection regulator releases formal findings, the details of the visits and the number of accounts affected remain unconfirmed information.