Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 ETH
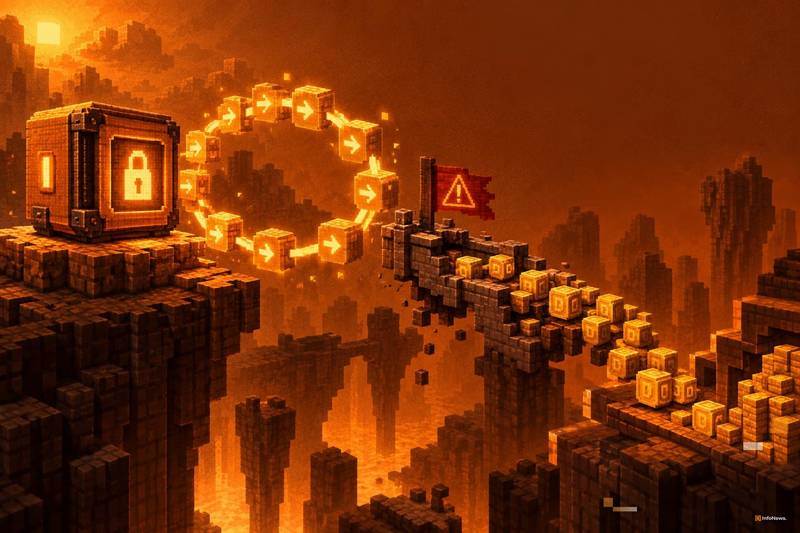
SlowMist points out that FlashLoopAdapter vulnerability caused Safe multi-sign wallet funds to be stolen.
Security company SlowMist said a vulnerability in the third-party adapter FlashLoopAdapter allowed attackers to withdraw collateral from two Safe multi-sign wallets. The incident highlights the risks of dependence beyond the core protocols DeFi users trust.
Specific impact of the FlashLoopAdapter flaw
According to CryptoSlate, SlowMist blamed the incident on a flaw in the FlashLoopAdapter. FlashLoopAdapter is a third-party component associated with the Aave v3 cycling feature. The company pointed out that the flaw was an entry point for attackers to transfer collateral out of two Safe multi-sign wallets.
This incident was also described in detail in SlowMist's alert about the Aave v3 Loop Safe module utilization incident involving 114.09 ETH. What is striking about the incident is that Safe Multi-Sign Wallet is widely regarded as one of the most robust hosting settings in Ethereum DeFi. However, the vulnerability does not originate from Safe itself or Aave's core contract, but exists in an adapter between the two.
Third-party adapters become attack surfaces
Reported flaws highlight a well-documented but often underestimated risk: DeFi's power stems from its composability, which also means that the security of a wallet or protocol depends on every external component it integrates. When a third-party adapter manages leveraged revolving positions on behalf of a multi-signature wallet, it has the right to move collateral; any flaws in the adapter can be exploited without touching the underlying protocol.
SlowMist's analysis strengthens the patterns the company points out in multiple ecosystems. Earlier this year, the company's chief information security officer warned of an iOS vulnerability targeting encrypted wallet keys and separately raised compatibility issues affecting Sui and Aptos, risks that lie at the integration layer rather than within the core protocol logic.
Teams and individuals that rely on multi-signature settings for vault or protocol hosting should audit every adapter and module granted permission to interact with their wallets and pay close attention to public security notices issued by SlowMist to understand newly disclosed vulnerabilities. The incident reportedly involved only two wallets, and SlowMist's report on CryptoSlate did not indicate a broader exposure; it is inaccurate to suggest a broader attack surface without evidence to support it.
For Bitcoin holders, this lesson clearly maps to the core security thesis of the UTXO model: self-hosting by minimizing external dependencies can reduce the surface area available to attackers. Every right granted to a third-party contract or adapter is based on assumptions that the adapter is correct, audited, and free of logical errors, and this incident demonstrates that this assumption may fail independently of the protocol it wraps. In addition, a random flaw in the Coinspect flag also demonstrates similar dependency risks across Bitcoin, Ethereum and Solana wallets, where the vulnerability exists in a shared library rather than the blockchain itself.