Bithumb 调查内部移动系统遭黑客攻击导致的数据泄露事件
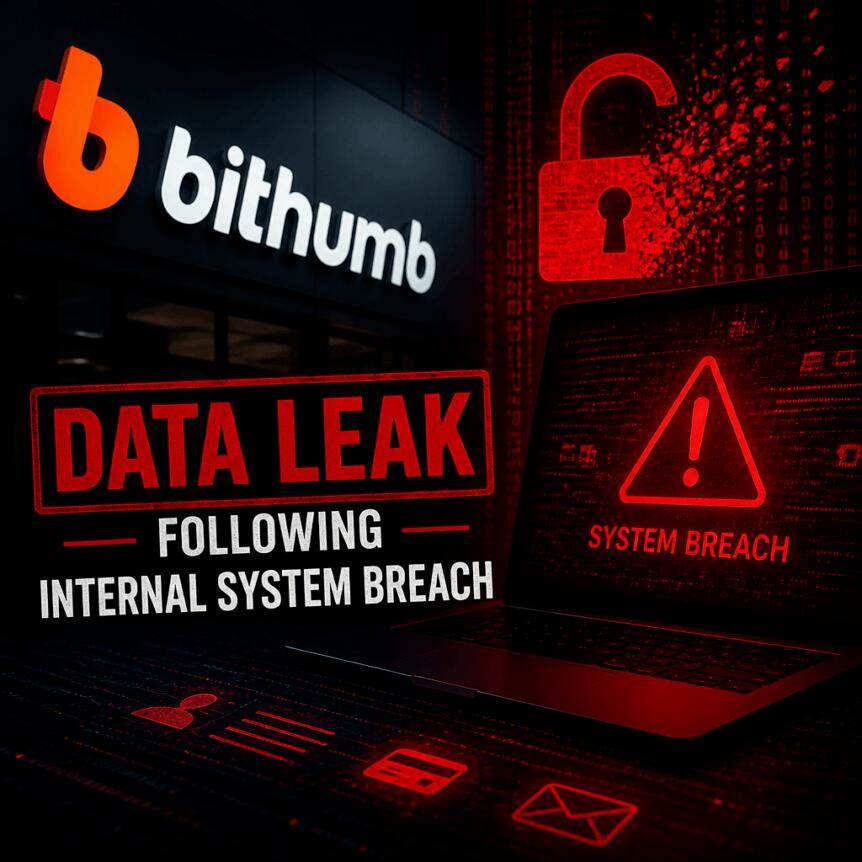
据韩联社周三报道,韩国加密货币交易所 Bithumb 正在调查本周早些时候其内部移动系统遭到黑客攻击所引发的数据泄露范围。
据报道,Bithumb 于周二发现了其内部移动系统(员工用于内部沟通的平台)遭到入侵,并于当天向韩国互联网与安全机构以及个人信息保护委员会通报了该情况。行业消息人士称,交易所正在调查此次攻击的范围,包括会员数据是否泄露。
Bithumb 向韩联社表示:“我们正在分析确切的影响范围,包括会员信息是否涉及其中。”“我们将于今日上午发布官方公告。然而,内部办公系统与虚拟资产交易系统是相互隔离的,因此客户无法通过此漏洞访问其虚拟资产。”
Cointelegraph 已联系 Bithumb 以获取进一步评论。
此次事件加剧了近期韩国金融行业遭受的网络攻击浪潮。在周三于金融监督院总部举行的会议上,院长李赞镇表示,截至 10 月 14 日,已有 16 家韩国金融机构遭受网络攻击。
《韩国时报》报道称,资产管理公司 Mirae Asset Global Investments 和大新证券也是近期网络攻击的受害者。大新证券表示,38,490 名客户的个人和信用信息遭到泄露。Mirae Asset Global Investments 则表示,它已阻止对部分网络系统的异常外部访问,并正在调查此事。据韩联社报道,该公司称投资者信息未受影响。
Disclaimer:
All content published on this website, including hyperlinks, related applications, forums, blogs, and other media accounts, originates from third-party platforms and their users. CoinMarketInsight makes no representations or warranties of any kind regarding the website or its content. All blockchain-related data and materials are provided for informational and research purposes only and do not constitute financial, legal, or investment advice. Users and third parties are solely responsible for the content they publish. CoinMarketInsight shall not be liable for any losses arising from the use of this website. You should exercise caution and conduct your own independent research, review, analysis, and verification before making any decisions.

 Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following