Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BNB
 BTC
 ETH
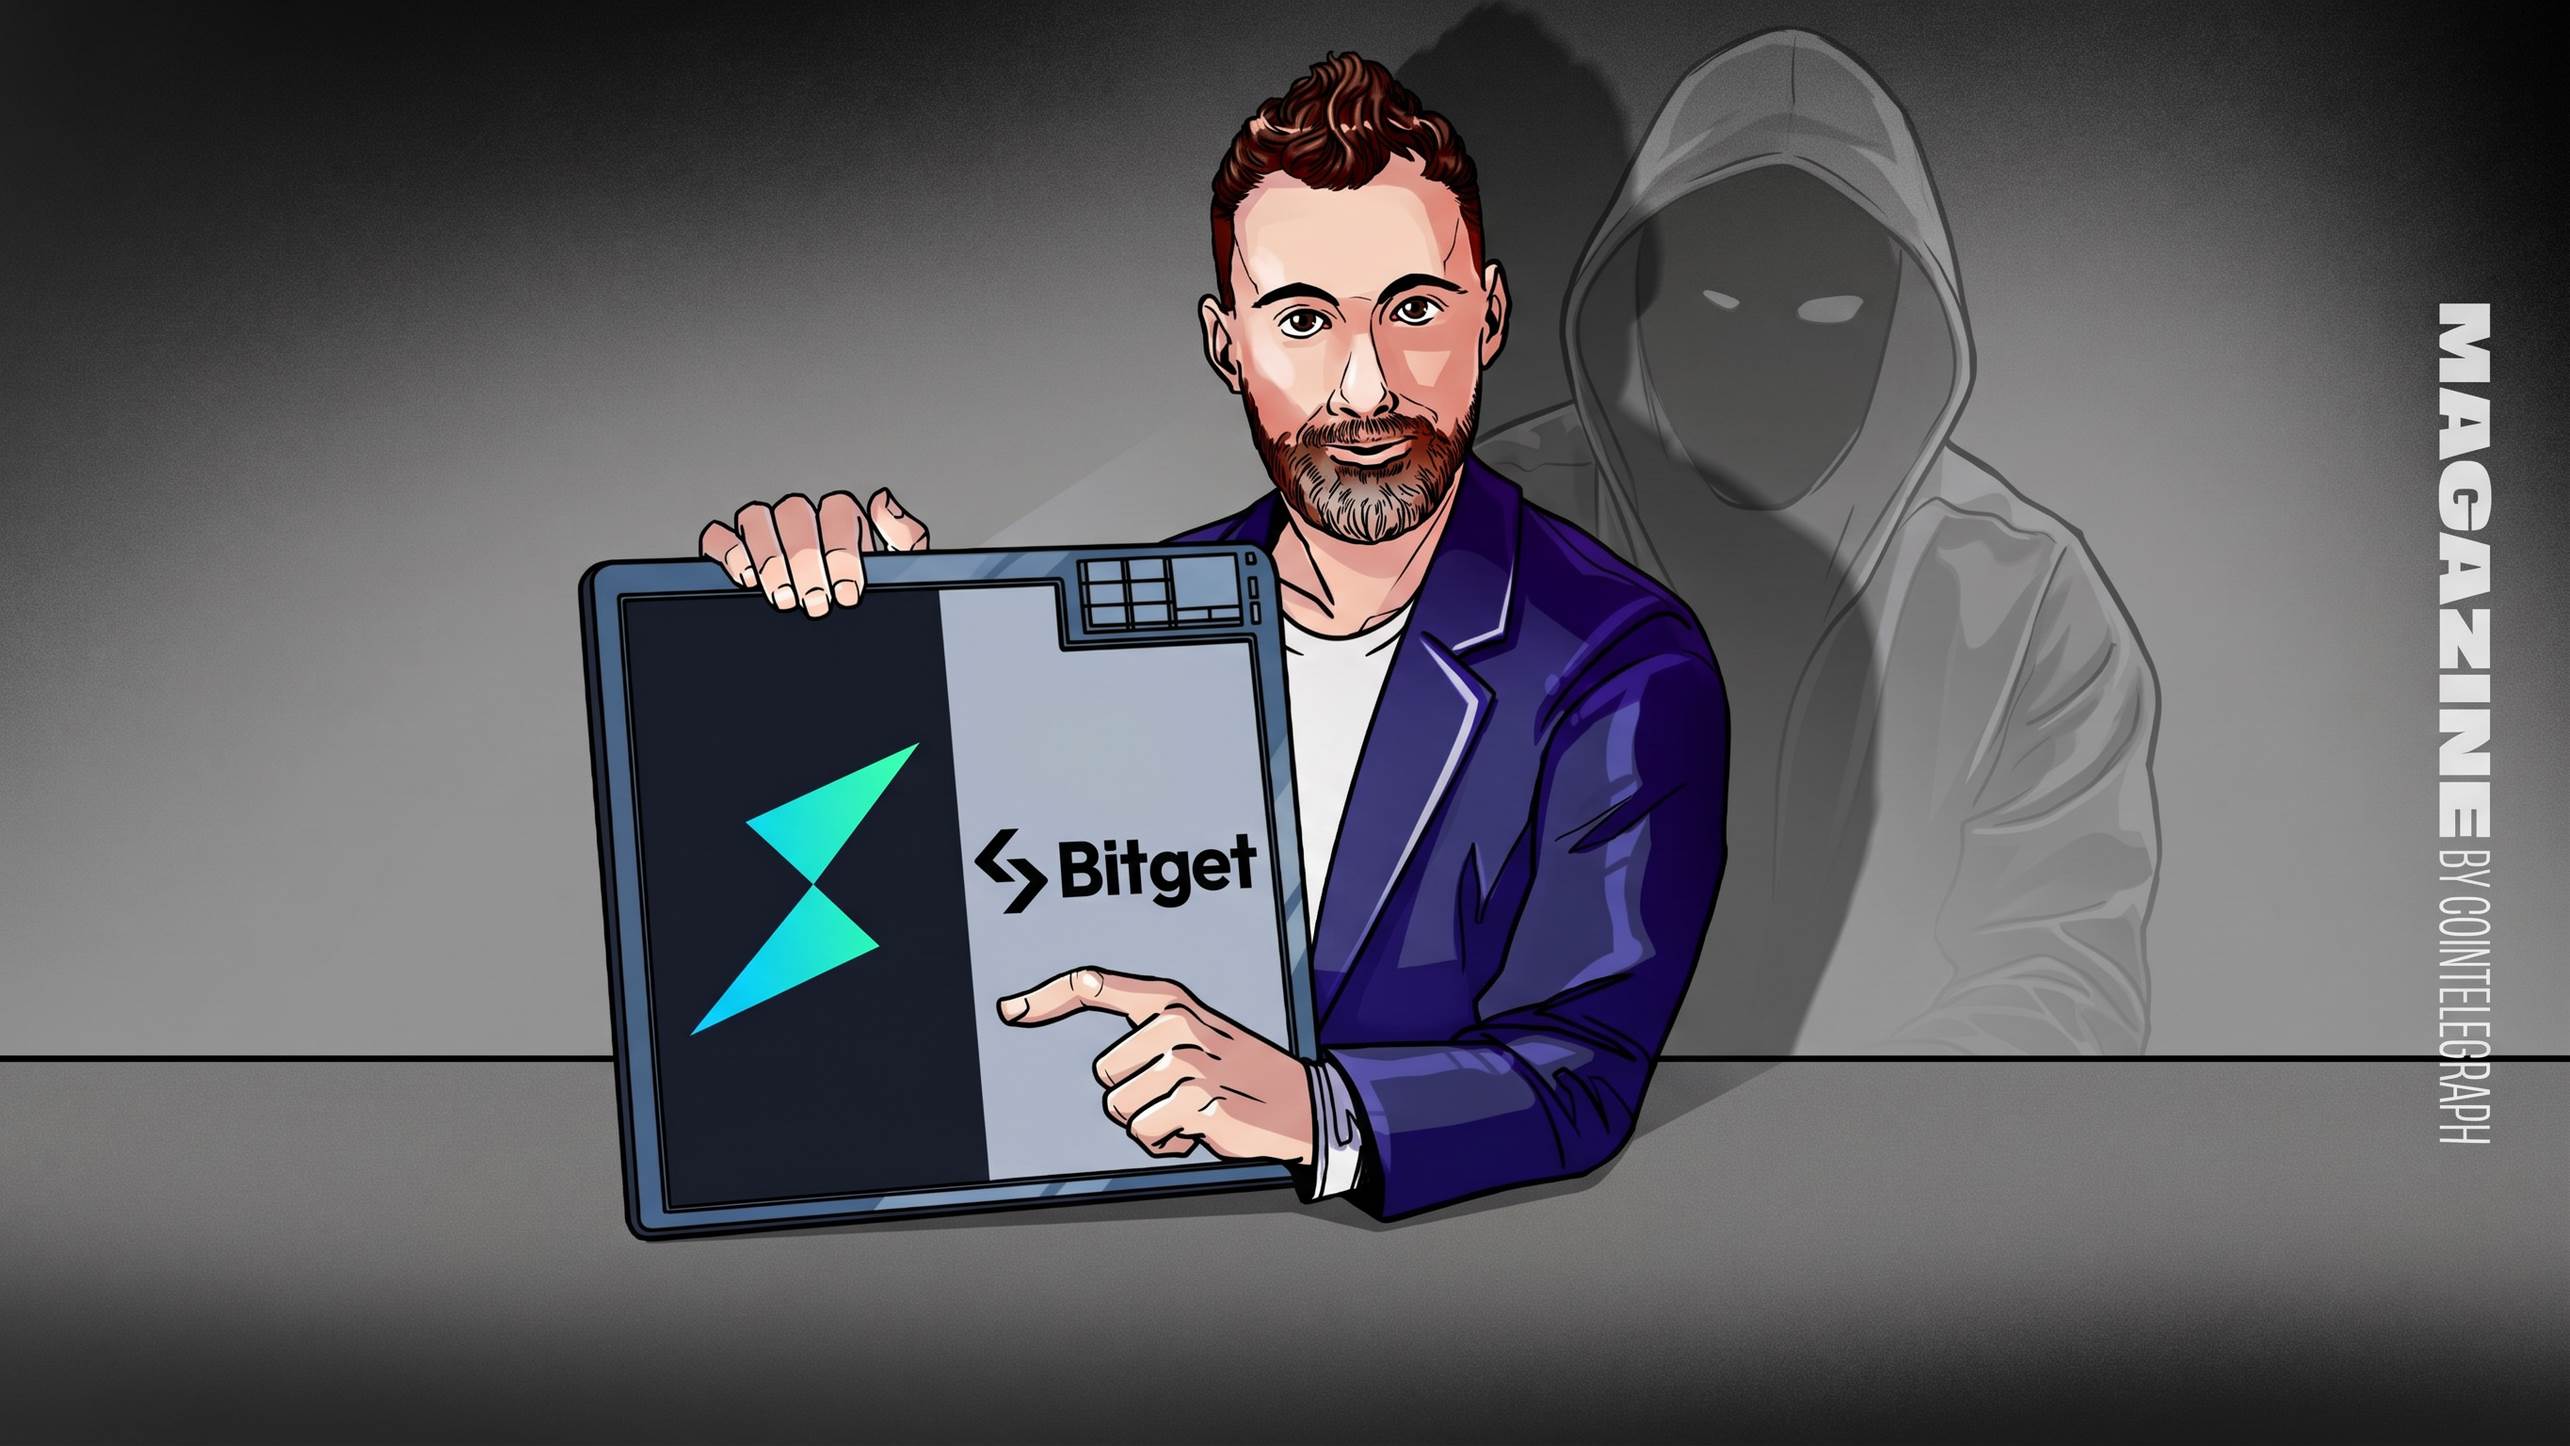
Bitget遭黑客攻击后,THORChain与NEAR Intents的合规困境:去中心化协议的法律边界
上周,疑似朝鲜黑客利用加密货币交易所Bitget漏洞盗取价值3.875亿美元的资金。随后,调查人员迅速标记并追踪了接收地址。Bitget首席执行官Gracy Chen随即引发争议,要求去中心化跨链互换平台THORChain“拒绝为这些地址提供服务”。
THORChain回应称:“THORChain像比特币、以太坊和BNB Chain一样,是去中心化和无需许可的。当处理已知被盗资金时,比特币、以太坊和BNB Chain应承担什么责任?”
这一举动颇具争议,尤其是在今年5月该协议因1070万美元自有资金被劫持而立即暂停之后。情况更为复杂的是,THORChain已退休其管理密钥(admin key),即使有意愿,也没有简便的方法来审查地址。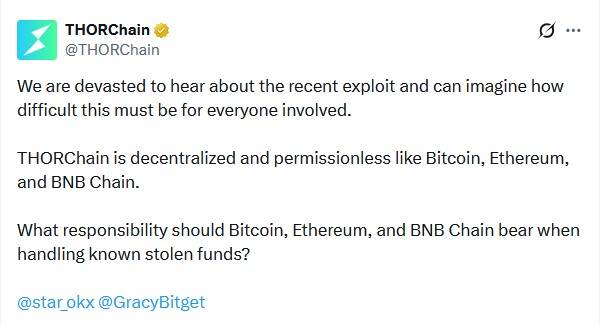
类似的争议此前曾出现过,当时THORChain被用于兑换Bybit 14.6亿美元黑客攻击事件中窃取的约12亿美元资金。巧合的是,THORChain的管理密钥恰好在11天前刚刚退休。
NEAR Intents采取了与THORChain相反的做法。其自动SHIELD程序阻止了与黑客攻击相关的地址在平台上进行5000万美元的兑换,甚至拒绝了Bitget为此提供的5%赏金。如今,NEAR Intents正因不够“无需许可”而受到去中心化极端主义者的抨击。
To discuss the legal issues involved in the case, we interviewed Yuriy Brisov of D&A Partners. The following is the edited content of the conversation.
Magazine:
Bitget asked THORChain to block funds associated with hacking attacks, and THORChain responded that it was decentralized and permission-free. Can this serve as a legal defense? Are they obligated to block these addresses?
Brisov:
It depends on the degree of decentralization. When they do this-that is, block certain addresses-they show that their nodes are not truly decentralized. Communities welcome this ability to prevent malicious activity, but at the same time they also expose themselves to any other legal claims. Their only protective umbrella is "We are decentralized."
In the Uniswap case, they claimed that 'we are truly decentralized and can't do anything about it.' (Investors sued Uniswap after purchasing 38 withdrawals and fraudulent tokens, but a judge dismissed the case in March-Editor's note.)
This is the strongest defense of any DeFi protocol. If they show they can prevent, control or intervene in some way-even in good faith to prevent fraud-they still face such claims. If you have control, then perhaps your control should not be limited to obvious fraud cases. You should imply control over due diligence matters. You should apply KYC (Know Your Customer) and AML (Anti-Money Laundering) protections.
Related reading: Uniswap defeats class action lawsuit suspected of aiding a cryptocurrency "withdrawal scam"
Magazine:
NEAR Intents阻止了这些地址,Bitget对此表示感谢。这是否意味着NEAR展示了Intents并非去中心化,因此需要在许多其他情况下进行干预?
Brisov:
如果你表现出对资产拥有控制权,那么你潜在地开放了自己,面对所有潜在的索赔,包括拉高出货方案、波动性,或任何投资者遭受损害和伤害的其他潜在索赔。他们现在可以说你拥有控制权。为什么你在一种情况下使用它,而在另一种情况下不使用?为什么不检查平台上的所有代币发行商?为什么不像任何中心化交易所那样提供KYC表格?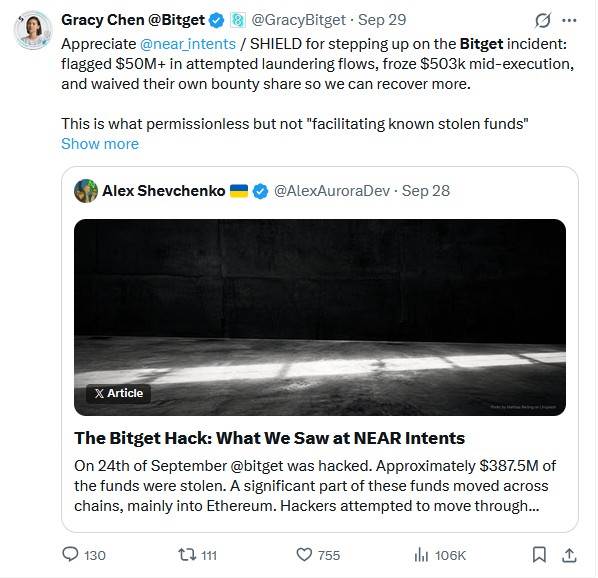
Magazine:
THORChain辩称,5月初的协议暂停最初由自动化系统触发,他们没有能力阻止特定地址。如果属实,这能作为抗辩理由吗?
Brisov:
这可能可以。我们还不知道,因为尚未受到挑战。但任何程度的控制都会使任何DeFi项目在面对任何索赔者时变得脆弱。
Magazine:
另一方面,如果协议希望阻止特定地址,它可以升级软件。如果项目不实施这样的措施,是否会因鲁莽或疏忽而陷入法律麻烦?
Brisov:
This depends on how it is implemented at the technical level. For example, there is a oracle that can detect any North Korean IP and automatically block it, and no one is sitting there pressing a button saying,"There is a North Korean hacker, let's stop him." then this is okay.
If there is a team monitoring the situation and saying,"Okay, we can see that this is illegal activity, we block these addresses and push the button manually." From a legal perspective, while this is a good act and benefits the community, it still makes the project less than completely decentralized in the legal sense and deprives you of the protections you receive, such as MiCA [European Union Crypto Asset Markets Regulation] or the general understanding of the SEC and CFTC that if you are completely decentralized, you are not responsible for the actions of ecosystem participants. 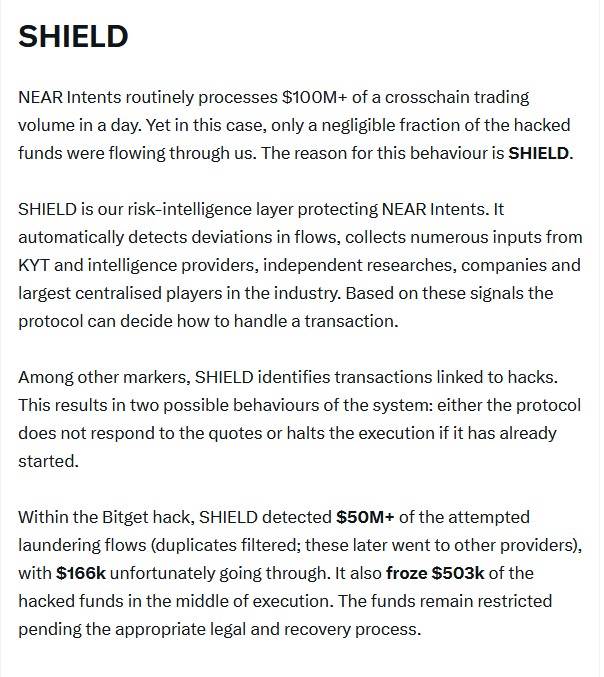
Magazine:
NEAR's technology is called SHIELD, an automated process that identifies addresses on the public blockchain that are associated with known hacking attacks and then automatically blocks them from accessing Intents. Does this mean it is more likely to be seen as decentralized?
Brisov:
Absolutely. They identified themselves as well-intentioned actors trying to add protections to the agreement. There is no compliance team and no one is sitting there to manually control operations. It's a smart solution, and it's what we recommend to all DeFi companies.
Magazine:
In February 2025, THORChain retired the management keys that allowed them to make such unilateral changes. Does the lack of administrative keys and having a hundred validators make them decentralized enough?
Brisov:
很有可能,但我们不能肯定地说。我会说是的。
Magazine:
THORChain不是混币器。你可以将被盗的Bitget资金在THORChain上兑换,但当资金出来时,它仍然透明地链接到Bitget黑客。这如何符合洗钱的定义?或者是收受赃物?
Brisov:
我不认为他们可以承担洗钱责任,因为即使是Tornado Cash,在一定程度上是为了洗钱而设计的[避免了美国制裁,因为不可变的智能合约在洗钱方面不属于可制裁财产——编者注]。
美国法律将某物视为财产或非财产。洗钱是通过合法渠道非法移动财产。你产生非法活动的收益,它是财产,然后通过某些渠道移动它并试图使其合法化。但智能合约根本不是财产。你不控制它们,也不拥有它们。这就是Tornado Cash在与OFAC制裁的官司中胜诉的原因。他们只是证明他们对智能合约没有任何控制权。
Magazine:
Bybit黑客攻击发生在18个月前。这意味着不会对THORChain采取任何法律行动,还是这些案件需要很长时间?
Brisov:
未来可能会发生, definitely。在Bybit案件之后,他们严重开放了自己,面临潜在的索赔。