Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
 WBTC
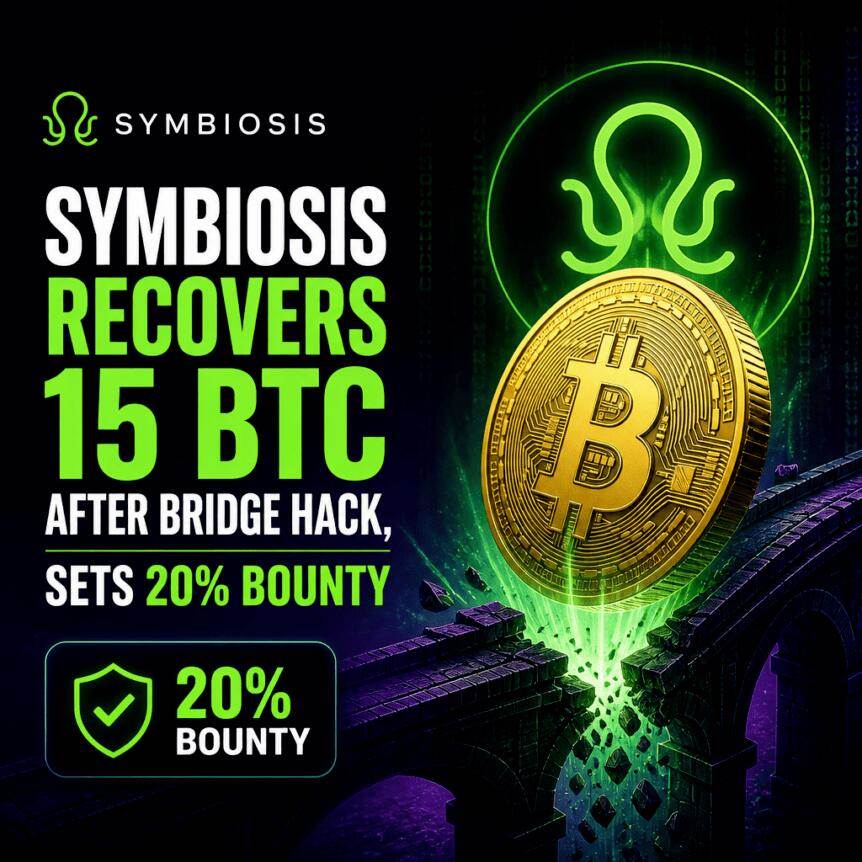
Cross-chain liquidity protocol Symbiosiss recovers 15 bitcoins after Bitcoin bridging vulnerability
Cross-chain liquidity protocol Symbiosiss announced that it has successfully recovered approximately 15 bitcoins (worth approximately US$1.1 million) after an attack on its Bitcoin bridging service. The agreement stated that the recovered funds had been transferred to multi-signature wallets controlled by the team. According to a post posted on Platform X on Friday, although the affected native Bitcoin bridge service remains suspended, all other routes remain operating normally.
This incident involved an attacker's address. According to analysis by blockchain monitoring company Blockaid, the address minted 46.1 billion unsupported tokens through Symbiosis's Bitcoin Bridge. Blockaid also reported that the attacker ultimately realized the value of approximately 4.3 Wrapped Bitcoin (WBTC) pieces, which equates to a price of approximately $336,000 at the time. However, Symbiosis has not clarified the specific relationship between the 15 recovered bitcoins and the proceeds.
Key Points
- Symbiosis reported that after the Bitcoin bridging vulnerability incident, 15 bitcoins (approximately US$1.1 million) have been recovered and deposited into a multi-signature wallet controlled by the team.
- The protocol means that all routes remain running, but its native Bitcoin bridge service is still suspended.
- Blockaid pointed out that the attacker made approximately US$336,000 in profits, but Symbiosis has not yet correlated this amount with the recovered funds.
- Symbiosiss has offered a 20% reward to sources providing asset recovery clues, exceeding the previous deadline for returning white hats that expired on Sunday.
- Independent tracking sites, including DefiLlama, estimated the loss at approximately US$336,000, but Symbiosis has not yet completed its final loss accounting.
Recovery of funds is in place, but bridging services are still suspended
Symbiosiss's latest update focuses on the operational status of its cross-chain systems. Its post on the X platform pointed out that the 15 recovered BTC had been deposited into a wallet controlled by the team through multi-signature hosting. The protocol also emphasizes that all routes are still running, indicating that users may still be able to operate through other components of the platform.
However, Symbiosiss stated that the native Bitcoin bridge service is still suspended. This is in line with the normal practice of such protocols that they need to stabilize the bridge logic, verify the balance, and ensure that the vulnerability vector is completely closed before resuming the bridge operation.
Blockaid's analysis of the vulnerability process
Blockaid's analysis points to a founding-based failure related to the Symbiosiss Bitcoin Bridge. Its tagged attacker addresses reportedly minted 46.1 billion unsupported tokens through bridges. Despite the huge number of mints, Blockaid pointed out that the net gain achieved by the attackers was only 4.3 WBTC, worth approximately $336,000 at the time of reporting.
Symbiosiss has admitted the vulnerability and the recovery of funds, but the agreement has not explained how to understand the relationship between the 15 BTC recovered and the $336,000 in proceeds Blockaid attributed to the attackers. This gap is critical for investors and liquidity providers: Without clear reconciliation information, it is difficult to assess whether the funds recovered represent full value at risk, partially recovered, or consist of a mixture of bridging assets that were later unpacked, converted, or reconstituted.
Suspenses to watch
Whether the total loss finally announced by Symbiosiss is consistent with DefiLlama's current estimates, and how it will handle the difference between the 15 recovered BTC and the US$336,000 attributed by Blockaid will be a focus of attention.
Reward incentives and unfinished loss accounting
In response to the vulnerability incident, Symbiosiss introduced a recovery incentive mechanism. The agreement said a 20% reward would be provided to any source of information that provides clues that lead to asset recovery. Symbiosiss had previously offered a similar 20% white-hat reward to encourage funds to be returned, but the deadline reportedly expired on Sunday.
Looking ahead, Symbiosiss said it will release a compensation framework for affected liquidity providers. For users, this is one of the most important next steps: Bridging events often lead to limited liquidity interruptions, potential risks to liquidity providers (LPs), and ripple effects for users who rely on stable routing.
DefiLlama's hacker tracking page recorded losses of approximately $336,000. Still, Symbiosiss has not provided final accounting data for total losses, which means public data may remain provisional until Symbiosiss completes its internal reconciliation and confirms whether there are additional losses in addition to Blockaid Highlighted gains.
Wave of vulnerabilities highlights ongoing bridging risks
Friday's incident is part of a broader pattern of bridging vulnerabilities that repeatedly test DeFi's resilience. Bridging-related vulnerabilities also made headlines earlier this year. In June this year, Symbiosiss was not an isolated case: Secret Networks suffered an "infinite casting" vulnerability attack that resulted in the theft of approximately $4.6 million. In May, the Verus-Ethereum Bridge was reportedly attacked by a fake cross-chain transfer vulnerability, losing 5,402 Ethers, valued at approximately US$11.6 million at the time. In this case, the attacker still retained approximately 75% of the stolen funds, or approximately 1,350 Ethers (approximately US$2.8 million), after the agreement provided a 25% white hat reward.
What connects these events is not just the money at risk, but the bridging-where assets often move between different accounting systems-can become the focus of verification failures, casting/destruction logic errors, or cross-chain message integrity issues. Even if an attacker ends up realizing only partial benefits, incidents can still trigger agreement suspensions, liquidity provider exposure, and time-consuming public reconciliation processes.
The case of Symbiosiss also illustrates a common asymmetry: the attacker may realize less than the initial theoretical damage, and the defender must then match the recovery details on the chain with off-chain accounting treatments and LP compensation plans. Before Symbiosiss provided the reconciliation, the true scope of the financial impact remained unclear.
Readers should pay close attention to two aspects of Symbiosiss next: detailed disclosure updates on total losses and recovered assets, and the compensation framework for liquidity providers. The long suspension of bridging services will also be a key indicator of whether the agreement can quickly restore full functionality without leaving residual risk.