Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
Ethereum researcher Justin Drake issued an urgent warning: AI and quantum computing may invalidate cryptographic signatures
Ethereum researcher Justin Drake recently re-emphasized the urgency that artificial intelligence (AI) and future developments in quantum computing may undermine cryptographic signatures used to protect cryptocurrency wallets. In comments published this week, Drake pointed out that the Elliptic Curve Digital Signature Algorithm (ECDSA) could be cracked in months rather than years, citing OpenAI's report on AI advances in mathematics as evidence.
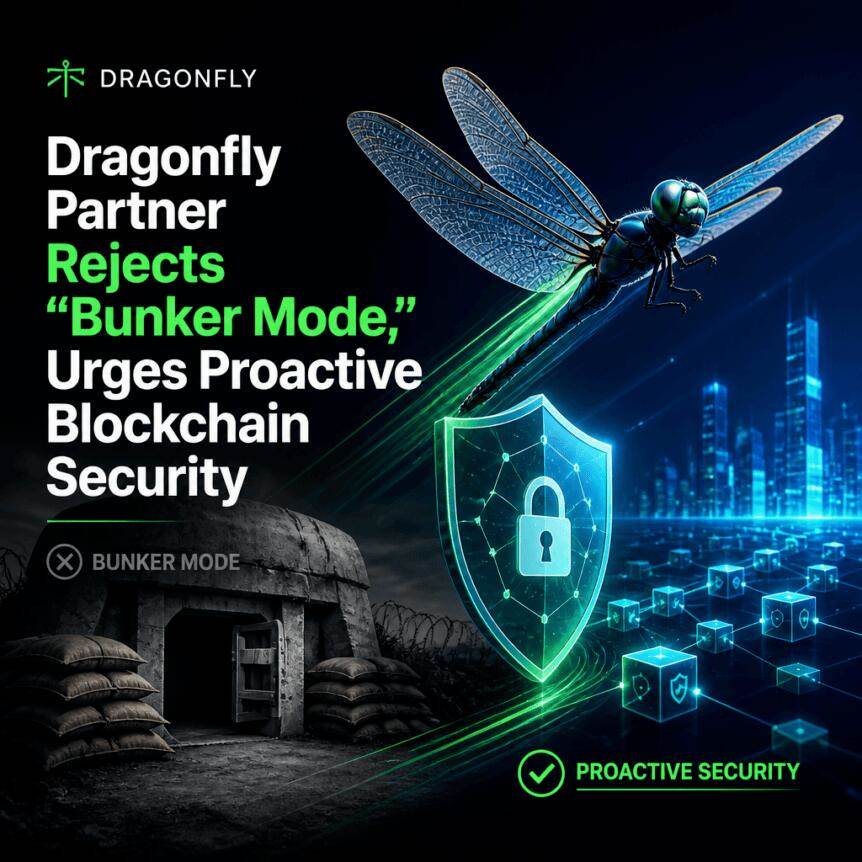
Haseeb Qureshi, managing partner of Dragonfly, refuted the narrow "move to new address" strategy. He believes that if the broader network ecosystem remains fragile, simply transferring funds to new public keys will not provide sufficient protection. Instead, Qureshi called for network-level security and proposed a "Cryptographic Recovery Mode" designed to help verifiers recover funds if signatures are compromised.
Summary of core points
- Drake's warning: Based on the rapid advancement of AI in mathematics, Drake warns that ECDSA may fail in a worst-case scenario within months rather than years.
- Qureshi's criticism: Dragonfly's Hasib Qureshi criticized the "bunker mode" as a remedy only for investors that cannot prevent large-scale asset damage if other participants remain exposed.
- Data support: cited Glassnode's data to indicate that 6.26 million BTC may be at risk, including 4.33 million funds related to address reuse.
- Solution Proposal: Qureshi proposes implementing a "cryptographic recovery model" that allows verifiers to forcibly recover funds through hash-based backup signatures.
Drake: "Months, not years"-Serious challenges facing ECDSA
Drake's latest comments focus on the ECDSA mechanism that underpins wallet authorization in many parts of the crypto ecosystem. He posted a post on Platform X (formerly Twitter) saying that it was "reasonable to expect" that ECDSA would be cracked earlier than many in the industry assume, with a worst-case time frame in months rather than years. Drake cited OpenAI's report on AI's progress in mathematics released Tuesday as a basis for taking this risk seriously.
Drake also recommends taking a practical user action: gradually transfer funds into new wallets to avoid exposing the associated public key. His views reflect a risk model that signature security may degrade faster than is typically considered in long-term migration plans-especially if AI accelerates the calculations involved.
Although Vitalik Buterin said he agreed that the industry should take AI-accelerated mathematical breakthroughs seriously, he disagreed with the rush to get users to immediately relocate funds into new wallets. The differences highlight a key tension in the current debate: what to do now versus what to do at the agreement and infrastructure levels.
Qureshi rejects the "bunker model" as a self-sufficient solution
Although Drake advocates migrating funds to avoid exposing public keys, Qureshi believes that the protection value of the new address is far less than the "bunker model" framework implies. In an X post on Thursday, he called Drake's warning "cryptographic doomerism" and argued that moving to a new address would be protective only if investors would never move those positions again after switching.
Qureshi's core concern lies at the entire network level. He warned that if cryptographic failure spreads beyond a small group of "fresh" holders-ultimately leading to mass theft and selling-even coins protected by newly generated addresses could become worthless in practice. In his view, if the underlying signature scheme becomes unreliable across the board, just protecting individual keys will not solve broader systemic problems.
Glassnode data: Millions of BTC at risk due to reuse and key exposure
这场讨论并非仅仅是理论上的。库雷希引用了来自 Glassnode 的数据,表明超过 31% 的比特币供应可能面临某种形式的暴露,具体指出了 626 万枚 BTC 处于易受攻击的地址中。
根据 Glassnode 联合创始人拉斐尔·舒尔茨-考夫特(Rafael Schultze-Kraft)的说法,在 626 万枚 BTC 中,约有 433 万枚因地址重用而暴露。在这种情况下,将资金转移到新地址可以消除与重用相关的风险。此外,约有 194 万枚 BTC 因地址格式而暴露,这是另一种不能简单地通过生成新地址来解决的向量。
舒尔茨-考夫特还强调了这些暴露头寸的分布情况。在总的暴露持仓中,近 180 万枚 BTC 存放在加密货币交易所,Glassnote 指出目前所有交易所余额中有 57% 是暴露的。这一点至关重要,因为交易所对于清算和托管流程至关重要;如果签名 compromised 成为现实威胁,处理高交易量的基础设施可能成为运营和风险管理的焦点。
从迁移到协议恢复:库雷希提出的“密码学恢复模式”
Qureshi believes that instead of relying solely on end-user migration, proactive network-level defense measures should be taken to deal with scenarios where cryptographic signatures are cracked due to AI-driven computing or future quantum capabilities. At the heart of his proposal is a "cryptographic recovery model" that describes a hash-based backup signature scheme that users can map to their addresses.
As outlined by Qureshi, the mechanism will allow verifiers to force the recovery of funds when cryptographic signatures are breached. The basic idea is to build a path that restores control even when normal signature verification is no longer trusted, shifting some of the security burden away from opportunity-dependent user actions.
This distinction is very important for investors and developers. Address migration is a mitigation strategy that depends on the user's response speed and whether the key remains secure after moving. In contrast, the recovery model aims to reduce the all-or-nothing nature of "new address" protection by introducing alternate structures at the verification layer.
However, several implicit uncertainties remain in the debate. Drake's proposal focuses on reducing exposed public keys, while Qureshi's counter-proposal relies on the design and adoption of a recovery process executable by a verifier. The impact of either approach on the market depends not only on the timetable of theoretical cryptography, but also on whether compatible standards can be implemented between wallets, exchanges and verification infrastructure.
As the timeline debate evolves, what is worth paying attention to next
德雷克关于“数月而非数年”的警告重新定义了围绕加密韧性的紧迫感,但对于业界而言,最可行的下一步可能是更清晰地规定钱包和网络应如何处理暴露问题——特别是对于由交易所持有的大量比特币。业界应关注后续工作,看如何将恢复概念转化为可实施的协议变更,以及获得关于如何在不过度增加运营风险的情况下快速实际迁移以减少暴露的指导。