Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 XRP
XRP Ledger 引入细粒度交易权限:在保留主签名密钥安全的前提下实现委托授权
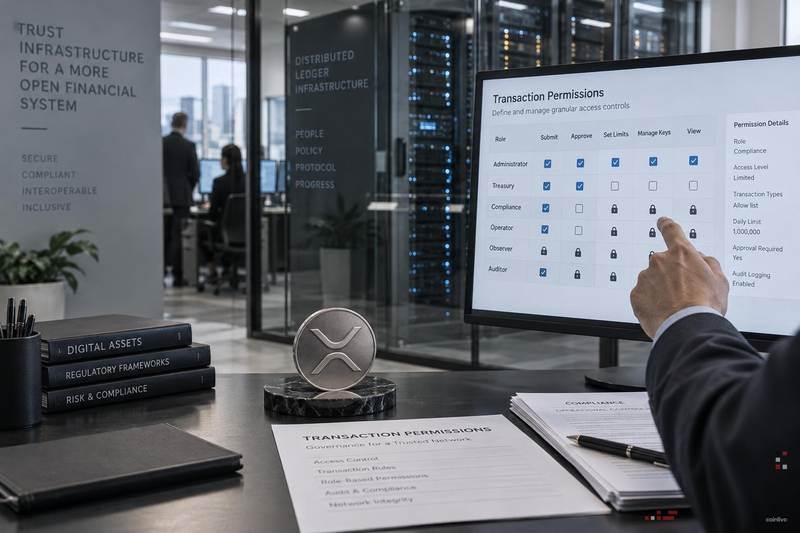
XRP Ledger(XRPL)正在新增细粒度的交易权限功能,允许账户持有者将有限的签名权委托给第三方、服务或自动化系统,而无需暴露账户的主签名密钥。此次更新旨在解决一个核心运营安全问题:即在向员工或应用程序授予日常交易访问权限的同时,确保所有者层面保持对账户的完全控制权。
核心要点
- 按交易类型控制权限:XRP Ledger 正在引入针对账户委托的每类交易权限控制机制。
- 作用域受限的凭证:委托凭证可限定于特定的交易操作,使主签名密钥脱离日常操作流程。
- 分离常规访问与完整权限:细粒度权限将日常访问权限与完整的账户控制权分离开来,从而降低单点故障的风险暴露。
为何主签名密钥会成为单点故障风险源
主签名密钥代表着对 XRP Ledger 账户的 unrestricted(无限制)权限。将其共享给任何服务、员工或自动化系统,意味着一旦该密钥遭到泄露或攻破,整个账户的资金可能被转移或被滥用。对于运行金库运营或支付流程的企业而言,接触该密钥的一方越多,这种风险敞口就越大。
The fine-grained permissions model solves this problem by allowing account owners to issue restricted credentials. Authorized parties only gain the right to perform specific defined transaction types, rather than having full access to the account. If the certificate is leaked, its scope of impact is limited to the allowed range and will not affect the entire account.
Scope access and separation of duties
Scope access draws on a mature principle in the field of enterprise security-the "minimum authority principle." Each delegation certificate is bound to a defined set of allowed actions. For example, payment processing services may be authorized to send transactions within set parameters, while the finance team retains exclusive access to account configuration changes or large transfers.
Permissions designed based on this model are not permanently valid. Account owners should treat it as an operating configuration that requires regular review, updates and revocation. As team structure, service integration, or risk appetite changes, those expired rights granted to no longer active vendors or services are themselves a risk factor.
Beneficiary groups and considerations before dependence
The clearest application scenarios are those that require employees or automated systems to perform repetitive, restricted transaction tasks but are unwilling to hand over master certificates. Wallet developers and application builders can also use scope permissions to reduce the need for full-scale key escrow, thereby reducing their own liability risk if the system is attacked.
As broader asset classes develop, XRP is gaining increasing institutional attention, including its presence in spot ETF discussions. Protocol-level access controls like these are a prerequisite for achieving institutional vault and custody integrations that make such products operationally viable.
Before relying on this feature, the team should verify which specific transaction types fall within the scope of authority, confirm how on-chain cancellations are handled, and establish an internal process for auditing active commissions. This update improves the security architecture of XRPL account management, but it is not a substitute for rigorous key management practices. Misconfiguration, lack of review, or authorization that is too broad will still reproduce the exposure of risks that this feature is designed to prevent.