Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
Apple App Store再次成为加密货币盗窃通道
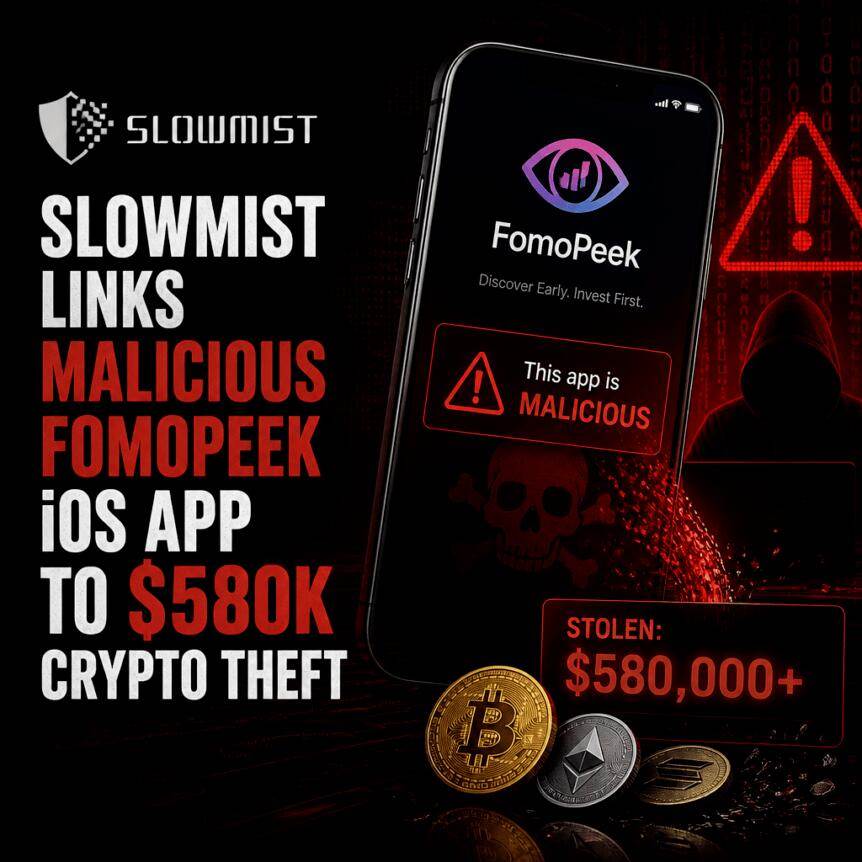
Apple的App Store再次被用作加密货币盗窃操作的传输渠道。根据区块链安全公司SlowMist的调查,一款名为FomoPeek的恶意iOS应用与近58万美元被盗加密货币有关联。攻击者利用内核级漏洞突破Apple的沙盒限制,从而获取敏感的钱包数据。
SlowMist指出,此次入侵针对的是特定版本的应用程序,而后续发布的版本移除了恶意组件。这一事件凸显了移动用户面临的持续风险:即使应用程序通过官方商店分发,操作系统层面的缺陷仍可能使攻击者访问本应受到保护的数据。
关键要点
- 损失规模: SlowMist将FomoPeek与约579,984 USDT的被盗资金联系起来,该应用在包含能够逃逸iOS沙盒保护的内核漏洞后导致了资产丢失。
- 受影响版本: 仅部分版本受到影响。SlowMist指出9月9日和9月12日的发布版本存在问题,而9月17日发布的1.3版移除了恶意模块。
- 目标数据: 恶意代码旨在获取受保护的数据。研究人员报告称,攻击者能够访问iOS Keychain数据以及其他应用程序的文件。
- 链上追踪: 资金在多个区块链网络间流动,随后通过多个地址和服务进行整合。
What SlowMest found in the FomoPeek app
In its threat intelligence analysis, SlowMest stated that FomoPeek contained multiple malicious modules designed to exploit iOS vulnerabilities. According to the report, the goal is to increase permissions and get rid of Apple app sandboxes.
Once an app gains such advanced access, SlowMist reports that it can access Keychain data as well as files from other apps. This is critical for users because Keychain entries often store credentials and other sensitive material used by wallets and related services-data that is often isolated from third-party applications.
SlowMist said the malicious components were part of the app version released on September 9 and September 12. The company added that version 1.3, released on September 17, removed harmful elements.
Release Time and Exposure Window
SlowMist's timeline suggests that the attack relied on users to install (or retain) the affected version of FomoPeek rather than the permanently damaged version. The company said its investigation began when it received reports of users who had experienced asset theft and confirmed that at least some of those users had installed one of the vulnerable versions.
This distinction is very important for practical risk management. Even if malicious applications are later patched or cleaned, damage is already done in early time windows-especially when applications can exploit kernel weaknesses and access protected data. The lesson for mobile users and wallet operators is that version-by-version review is as important as store-level distribution.
漏洞框架细节及受影响的iOS范围
SlowMist表示,其观察到的漏洞框架具有八种攻击方法。报告描述了广泛支持一系列iOS版本的意图,包括12.0至18.7.2以及26.0至26.1。
这些范围的广度强调了为何内核漏洞利用如此难以遏制。当攻击者可以针对多种配置时,同一个恶意应用程序可能在更大比例的安装基础上发挥作用,增加了成功入侵的可能性。
链上分析:近58万美元被盗加密货币
除了应用程序端的发现外,SlowMist还分析了相关的区块链活动。该公司确定了与该事件相关的一个主要黑客地址,接收了约579,984 USDT。
根据SlowMist的说法,该地址于9月15日活跃——这是在初始受影响版本发布之后——这表明盗窃活动发生在用户可以安装易受攻击版本的时期之后。SlowMist进一步表示,被盗资金分散到多个区块链网络上,然后通过其他地址和服务进行整合。
SlowMist报告称,部分资金流向包括FixedFloat、KuCoin和cce.cash等服务,而其他部分则通过该公司继续追踪的其他地址分散。
对于投资者、交易员和合规团队来说,这种模式通常是掩盖资金轨迹的努力的典型特征:攻击者经常在跨网络之间转移价值,通过中介碎片化流程,然后以难以归因的方式整合收益。
尝试获取回应
Cointelegraph表示已联系Apple、SlowMist和OKX寻求评论。该媒体报告称,在出版前未收到回复。
据报道,SlowMist的调查是与OKX安全团队共同进行的。这种合作表明了加密货币应急响应如何日益融合链上取证与软件安全研究——特别是在攻击起源于像应用商店这样的主流分发渠道时。
在9月17日报告的移除之前在iOS上安装FomoPeek的用户应考虑审查钱包权限,并检查是否有任何账户显示未经授权的活动。未来存在的关键不确定性在于,除了SlowMist确定的特定版本外,是否存在其他恶意版本或相关包——以及Apple或更广泛的移动安全社区是否会加速防御通过应用商店软件交付的内核漏洞利用。