Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
 ETH
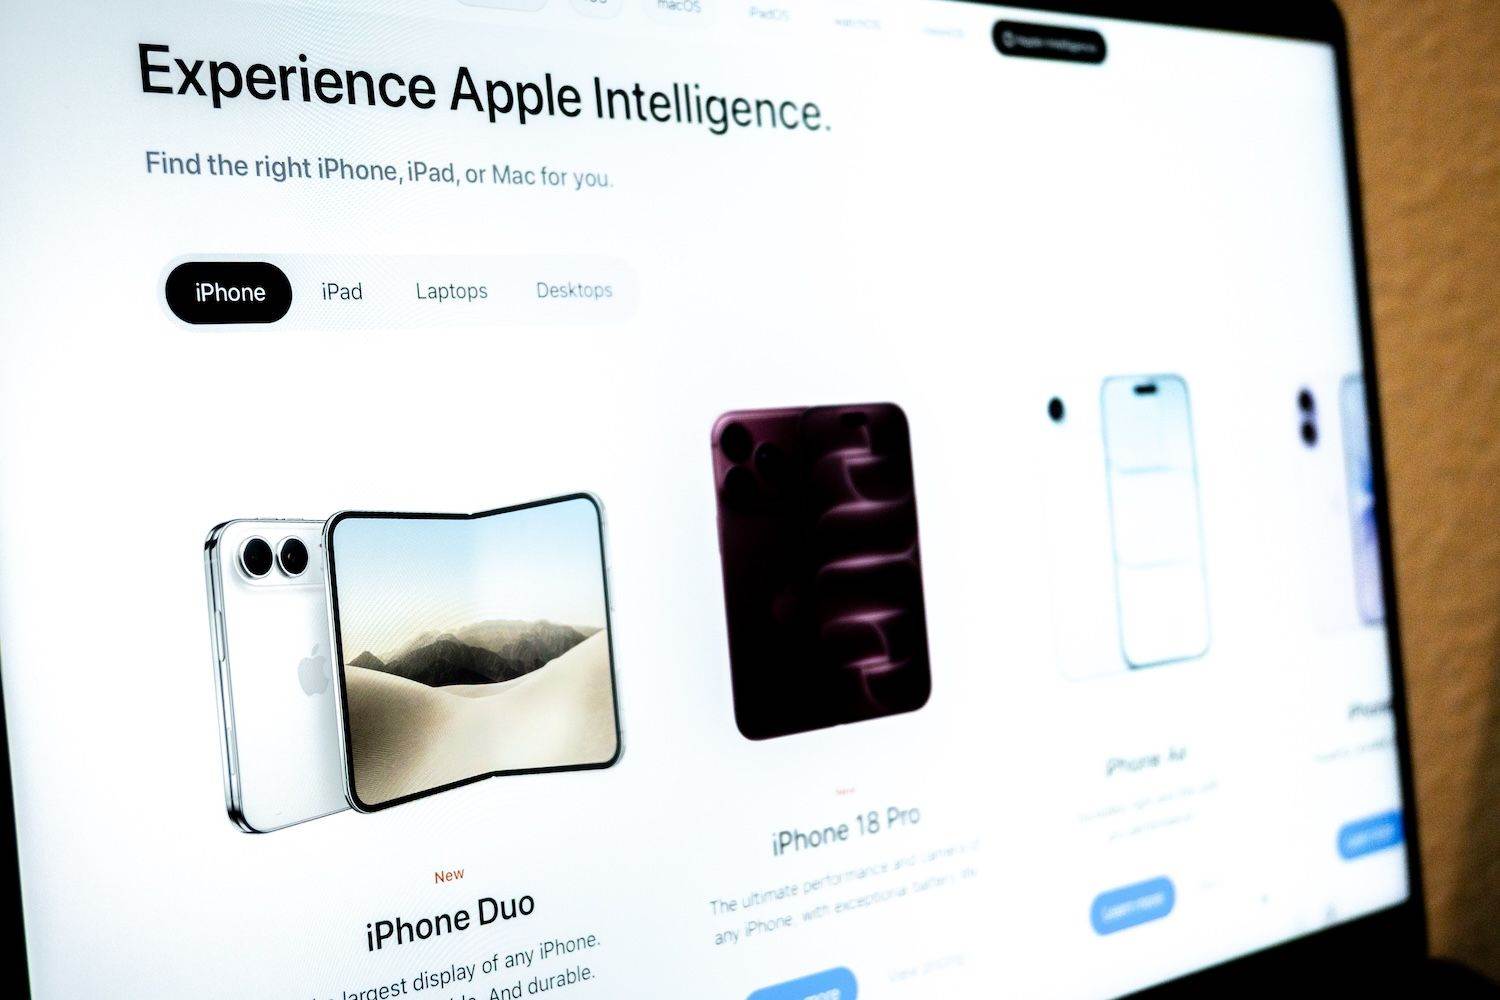
Security researchers discovered that a fake "iPhone Duo" pre-order page was used to attack vulnerable devices and encrypted wallets using $500 coupon bait.
Core points:
- When a vulnerable iPhone accesses the page, a malicious attempt is immediately initiated.
- The payload is designed to steal encrypted wallets, keychain certificates, memos and other personal data.
- Apple said the updated device's system is resistant to the reported "DarkSword" attack.
"iPhone Duo" Fraud Disclosure
Security researchers at Malwarebytes discovered this counterfeit Apple-style webpage while tracking fraudulent activity related to the release of "iPhone Duo." The relevant survey results were released on September 29 and subsequently reported by technology media.
The site claims to offer $500 worth of "authorized partner-only" coupons and AppleCare+ service coverage. However, pre-orders for the official "iPhone Duo" will not actually start until October 16.
Malwarebytes pointed out that the device size and color scheme listed on the fake page are inconsistent with Apple's official product line, and several policy links included on the website do not work properly. What's even more dangerous is that malicious exploitation attempts are initiated automatically before a visitor submits any information. Researchers said the page used a leaked "DarkSword" attack chain to detect vulnerable iPhones, and then attempted to load a separate payload to collect device information, Apple memo content, and saved keychain credentials.
Malwarebytes Wallet Risk Analysis
The payload of this malware searches for multiple cryptocurrency wallet applications including MetaMask, Phantom, Trust Wallet, Coinbase Wallet, Exodus and Tonkeeper. If it successfully connects to the attacker's server, it will attempt to upload wallet files, credentials, and photo thumbnails.
The researchers also found that the code contained stealing logic for text messages, contacts, call logs, voicemail, emails, calendar entries, and cached location data. In addition, the payload can contact its control server for further instructions.
Malwarebytes said they analyzed the captured code, but did not test it on an actual iPhone and did not observe data leaving the device. This limitation means that the researchers confirmed the logical structure of the attack rather than confirming the successful theft of data from the victim.
Google disclosed the "DarkSword" vulnerability in March 2026, and Apple subsequently fixed the reported security issues in the same month. At the time, an evaluation agency estimated that as many as 270 million devices were running the affected versions of iOS. However, Malwarebytes pointed out that the data is no longer accurate and the specific range of vulnerable devices targeted by this page has not been confirmed.