Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
 ETH
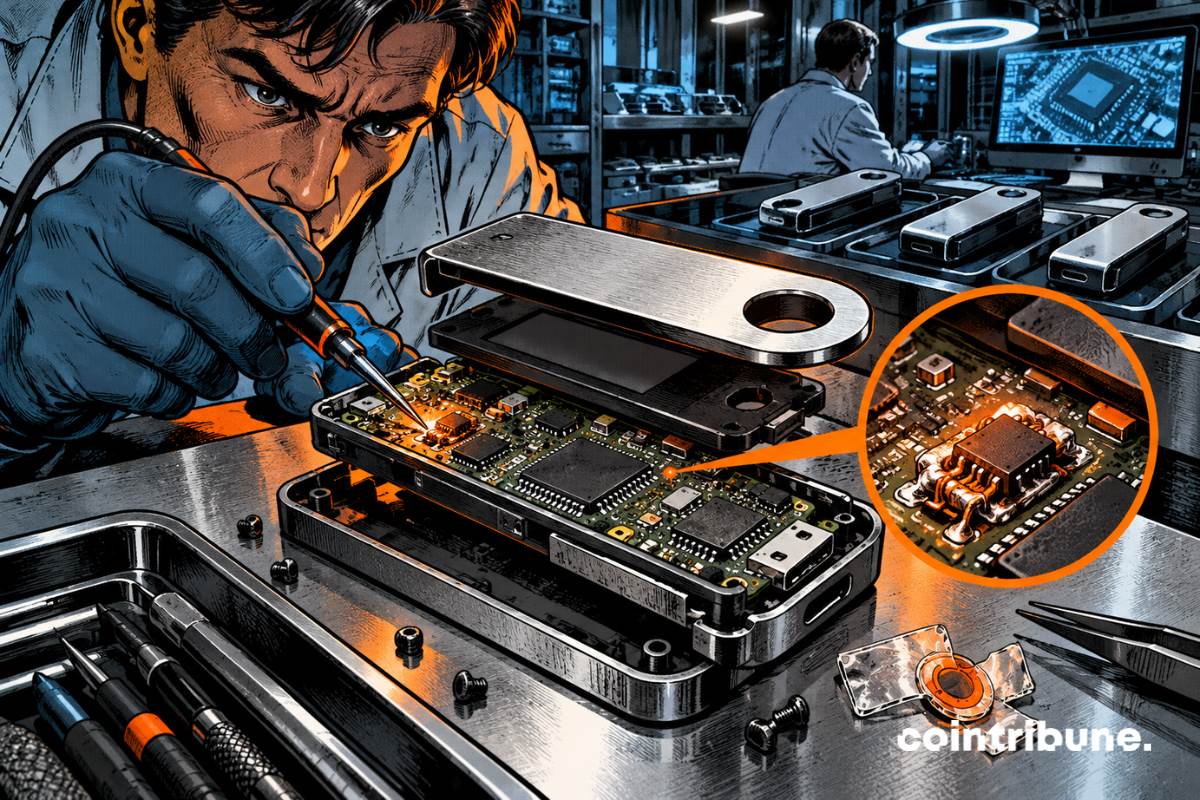
Ledger事件出现新转折:确认用户设备遭硬件植入物篡改
加密货币钱包制造商Ledger证实,在东南亚近期被盗案件受影响的一名用户的设备中发现了未经授权的硬件植入物。这一发现使得“产品在交付前遭到物理篡改”的推测进一步得到强化。目前嫌疑损失金额已接近9,300万美元,但该数据尚未得到Ledger官方验证。
事件概要
- Ledger确认至少一名受影响用户的设备中存在硬件植入物。
- 独立分析师估算加密资产损失高达9,340万美元。
- 经销商CryptoBilis已在调查期间暂停其硬件钱包的销售业务。
实体篡改假设获有力佐证
此前几天,Ledger仍在调查中,并未确认事故原因。当时有超过8,600万美元的损失与从东南亚经销商CryptoBilis购买的钱包相关联。10月10日(周六),公司提供了更具体的证据:一台属于受影响用户的设备中包含一个未经授权的硬件植入物。这一发现严重加强了供应链攻击的假设。
CryptoBilis曾在印度尼西亚、马来西亚和菲律宾等地销售Ledger设备。Ledger已要求其在调查期间暂时停止销售和发货,该经销商随后暂停了所有硬件钱包的销售。
Ledger emphasizes one point: There is currently no evidence of damage to its infrastructure, systems or internal services. This distinction is crucial. Problems can occur after manufacturing, at some point between the manufacturer and the end user.
Implants can steal mnemonic words and endanger financial security
Prior to official confirmation by Ledger, former Mt. Mark Karpelès, head of Gox, once posted pictures showing a modified Ledger Nano X. He allegedly found a hidden small circuit board behind the screen that contained cellular communications components.
The way this implant works poses a serious threat to the security of cryptocurrencies. It does not need to crack Ledger's Secure Element, it only needs to monitor the information sent to the screen during wallet setup. It is at this moment that the 24 recovery mnemonic words appear. Once the phrase is intercepted, an attacker can theoretically rebuild the wallet and transfer assets on another device without the need for the original Ledger device.
The device may even leave the original encryption chip intact. Equipment that has undergone such modifications is likely to appear authentic in some inspections. The case reveals another aspect of supply chain attacks. As early as 2025, Ledger's chief technology officer warned that NPM package tampering threatened cryptocurrency users. This time, the problem is not hidden in the software, but directly exists at the hardware level.
Nearly US$93 million in crypto assets at risk
相关数据仍在不断变化。Yfarmx估计涉嫌损失约为9,340万美元,涉及471个地址;Bitquery统计约为9,290万美元,涉及311个唯一地址。Ledger尚未确认任何总数,也未确定每个被计数的地址都对应一台经过物理修改的设备。截至目前,Ledger仅公开确认了一台属于受影响用户的设备存在植入物。
比特币、以太坊及多种稳定币均被列入可疑交易追踪名单。Ledger建议最近从CryptoBilis购买设备的用户不要开始设置流程。对于已经使用的用户,公司建议将资产转移到使用新助记词的新签名设备上。如果在助记词已被截获的情况下将相同的24个单词重复用于新设备,显然无法解决问题。
Ledger正在研发针对物理篡改的新保护措施。此事件发生时,硬件钱包正作为将加密货币密钥与中心化平台隔离的解决方案进行推广。然而,没有任何系统能保护所有场景。今年早些时候,一款假冒Ledger应用曾导致近950万美元加密资产被转移。此次攻击方式不同:用户可以遵循常规规则,离线保存助记词,且不签署任何可疑交易。但如果设备在到达前已被篡改,威胁便早已存在。这正是Ledger现在必须确定的关键问题:有多少设备遭到篡改、何时发生以及由谁实施。