Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 AVAX
 BNB
 ETH
 XRP
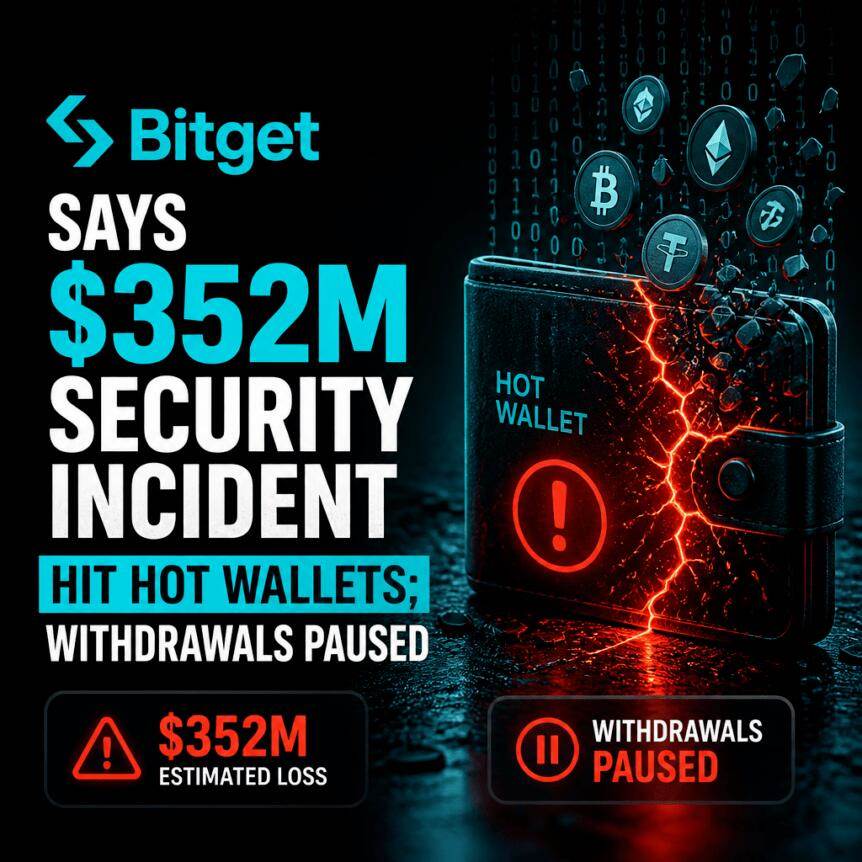
Bitget确认遭遇安全漏洞:约3.516亿美元资产受波及,提现暂停
Crypto交易所Bitget已确认检测到与其安全漏洞相关的未经授权转账,并在调查期间暂时停止了提币服务。该交易所表示,此次事件影响了价值约3.516亿美元的资产,但仅限于部分热钱包持仓。
Bitget报告称,其系统于周四UTC时间18:31识别出可疑活动,随即触发了应急响应措施。为了遏制损失扩大,公司指出此次入侵仅限于某些热钱包和温钱包层级,而冷钱包保持安全。
关键要点
- Bitget表示,未经授权的交易影响了约3.516亿美元的资产,这些资金可追溯至数量有限的热钱包。
- 在检测到UTC时间18:31的活动后,该交易所暂时停止了提币服务,并正在进行安全审查。
- 首席执行官Gracy Chen表示,受影响资金主要集中在以太坊(Ethereum)网络上,其他涉及的网络还包括XRPLedger、Avalanche、BNB Smart Chain以及Arbitrum。
- Bitget声明用户余额准确无误,存款和交易功能正常运行。
- Chen表示,受影响资产的规模已超过Bitget“用户保护基金”的覆盖范围,该基金目前持有超过4.64亿美元。
热钱包层级检测到未经授权转账
Bitget issued a statement on the X platform saying its security monitoring system detected unauthorized transfers from a small number of hot wallets. The company linked the activity to an Incident Response Service program that was activated immediately after the alert was issued and noted that the incident occurred at 18:31 UTC on Thursday.
During the live Q & A session, CEO Gracy Chen emphasized that the intrusion was limited to some of the exchange's hot money packages and warm wallet infrastructure. She also said Bitget's cold wallet had not been compromised.
According to Chen, the stolen or affected assets include Ether (ETH), XRP (XRP), USDt (USDT), USDC (USDC), Avalanche (AVAX), BNB (BNB), and USDT0 (USDT0) on Arbitrum. She pointed out that the largest scale of stolen funds observed was concentrated on the Ethereum network.
Multiple chains are involved, with Ethereum as the main concentration place
Chen listed multiple affected networks, including Ethereum, XRPLedger, Avalanche, BNB Smart Chain and Arbitrum. While Bitget highlighted Ethereum as the main venue for observed stolen funds, the exchange also reported activity in other ecosystems, suggesting that attackers were operating in multiple wallet and chain configurations rather than targeting a single isolated target.
Bitget's communication also acknowledged that there were differences between early on-chain reports and subsequent disclosures. Chen said that because the incident exceeded the scope of Ethereum activity as reflected in the initial trace, the amount captured by early on-chain surveillance was less than the amount subsequently reported by Bitget. This distinction is critical for traders and users, as estimates of the size of the vulnerability may change as investigators expand their analysis window and expand their search beyond the first chain cluster initially detected.
Withdraws suspended; deposits and transactions continue
Bitget said it has temporarily suspended the withdrawal service as part of a security review. Chen said it expected withdrawals to resume within hours or days and viewed the suspension as a precautionary measure so that exchanges could verify controls and assess the scope of unauthorized movements.
At the same time, Bitget informs users that their account balances are still accurate. The exchange also said deposit and trading functions are operating normally, an important operational detail for customers who may expect the platform to be completely shut down in the event of a security incident.
The exchange said it had marked addresses associated with transfers and contacted law enforcement and chain security companies, which is consistent with the exchange's typical process for responding to suspected theft-identifying suspicious sources, tracking downstream flows, and coordinating removal or mitigation efforts if possible.
User protection funds will cover affected assets
In addition to control and monitoring, Bitget also directly addresses customer risk issues by citing its "User Protection Fund." Chen said the size of the funds affected exceeded the fund's coverage, and the exchange said the fund currently holds more than $464 million.
Bitget also said it will provide hourly updates to reflect ongoing investigations. In addition, the exchange promises to release a complete incident report within 24 hours, including root cause analysis and corrective actions. For users and market participants, these deliverables are particularly important: A clear explanation of what caused unauthorized transfers to occur-such as weaknesses in wallet controls, key management, operating processes, or monitoring-can determine whether the incident is isolated or a sign of broader systemic risk.
As the investigation progresses, readers should pay attention to whether Bitget's promised incident report supports its claim that only the Hot Wallet and Warm Wallet levels were affected, and whether the exchange's address tags produce measurable mitigation effects along the chain. The next few updates may clarify the exact vulnerability mechanism and confirm when withdrawals will resume.