Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
Coldcard hardware wallet firmware vulnerability causes $116 million in Bitcoin to be stolen
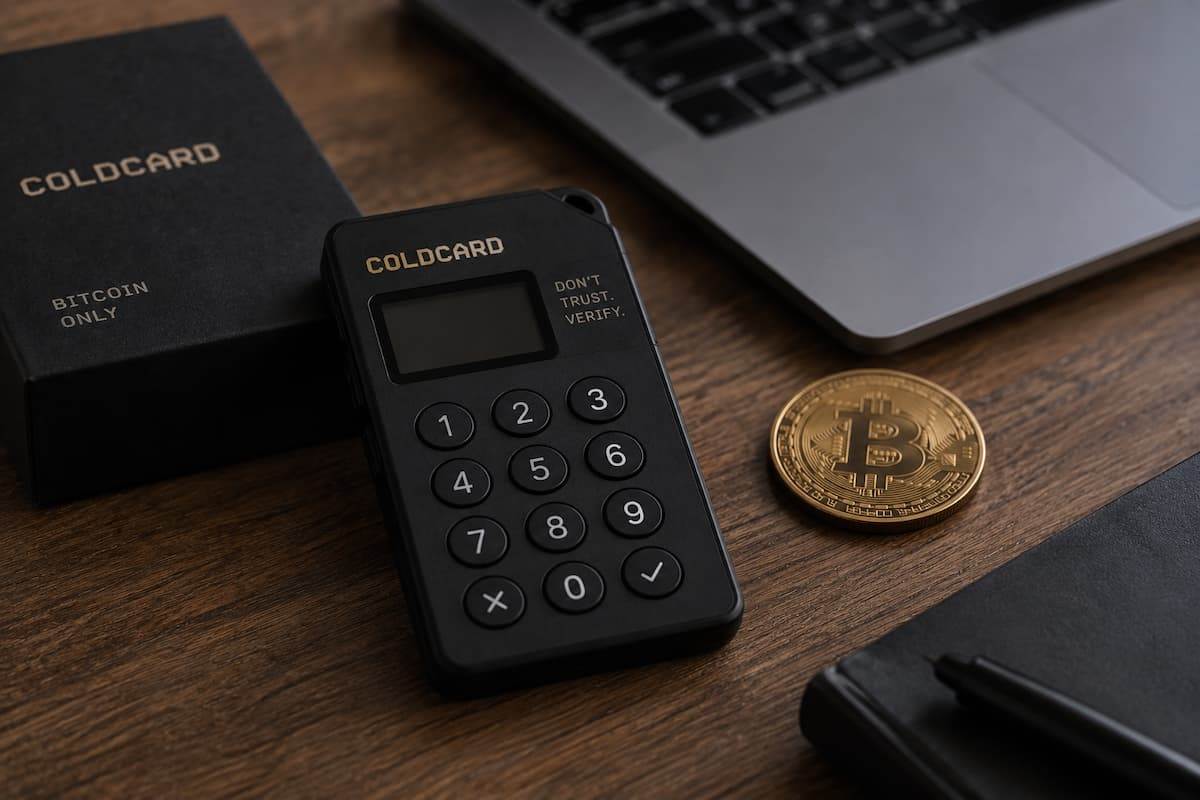
A firmware flaw in Coldcard hardware wallet was exploited by hackers, resulting in the theft of approximately $116 million in Bitcoin. The incident has been described as the largest theft of hardware wallets recorded in 2026. The incident broke the widely believed security assumption that offline, physically isolated storage is immune to remote attacks.
The existence of hardware wallets is based on a core premise: storing private keys on dedicated offline devices is more difficult to steal than private keys stored on connected computers or mobile phones. However, this year this premise has been severely impacted. Coinkite's Coldcard, one of the widely used devices among Bitcoin holders who focus on self-custody, was exploited and approximately $116 million in Bitcoin was stolen. This is the largest hardware wallet-specific theft case tracked by blockchain intelligence company TRM Labs in 2026.
Breaking the safety myth of "air isolation"
The reason why the Coldcard case is worth studying is that it breaks the inherent perception of most holders of air isolation devices: that is, devices without network connections cannot be hacked remotely. The firmware level flaw completely changes this security logic, because firmware is software that runs directly on the device itself, controlling how transactions are signed and how they interact with stored keys. A vulnerability at this layer does not require a real-time network connection to cause harm; it only requires the existence of a path-whether through malicious updates, constructed transactions, or vectors processed by other devices-to trigger unexpected behavior in the code, directly threatening code that has rights to the wallet's private key.
An analysis of this attack points to the dangers of concentrating such a huge amount of authority in a single firmware, especially the lack of sufficient independent verification mechanisms before execution to determine what the firmware actually performs. Hardware wallets often rely on their physical isolation from the Internet as their main selling point, but this isolation protects users only if the firmware itself has no exploitable flaws, because the entire security model is based on the assumption that "the code is running exactly as expected." Once a vulnerability appears in this layer, the offline nature of the device no longer constitutes an effective defense.
Industry reflection and safety enlightenment
The scale of the theft and its targeting of the device category deliberately chosen by security-conscious holders have forced the industry to refocus on auditing hardware wallet firmware. For manufacturers that rely heavily on their reputation for physical isolation as a core security strategy, incidents like this raise a serious question: Are their firmware review and update processes rigorous enough to detect and fix such serious flaws before major losses occur, rather than waiting until a nine-digit theft forces the problem to be exposed before taking action.
The practical lesson for holders is not that hardware wallets are unsafe, but that there is no alternative to the importance of keeping firmware updates and paying attention to manufacturer security disclosures. The strength of a device purchased for its offline security guarantees depends only on the firmware version currently running. Security breaches discovered after purchase do not retroactively protect exposed funds. The Coldcard incident reminds us that self-hosting shifts the responsibility for security onto the holder, and that responsibility clearly includes tracking firmware level risks, rather than just physically ensuring the security of the device.