Exchange Ranking
 Top Exchanges
 24h Volume Ranking
 Popularity Ranking
 Exchange BTC Balance
 Proof of Reserves
 Decentralized Exchanges
 Funding Rate
 Funding Heatmap
 Liquidation Data
 Max Pain
 Long/Short Ratio
 Whale L/S Ratio
 Binance/Okex/Huobi L/S
 Bitfinex Margin L/S
 ETF Tracker
 Solana ETF
 XRP ETF
 Hong Kong ETF
 Bitcoin Treasuries
 Crypto Reversal
 Ethereum Reserves
 HyperLiquid Wallet Analysis
 Hyperliquid Whale Watch
 Large Transactions
 On-chain Movement
 Bitcoin ROI
 Stablecoin Market Cap
 Options Analysis
 News
 Articles
 Economic Calendar
 Features
 Wallet
 Contract Calculator


 Security
 Collections
 Watchlist
 Following
 BTC
 ETH
Ledger确认在客户设备中发现未授权硬件植入物,引发对硬件钱包供应链完整性的担忧
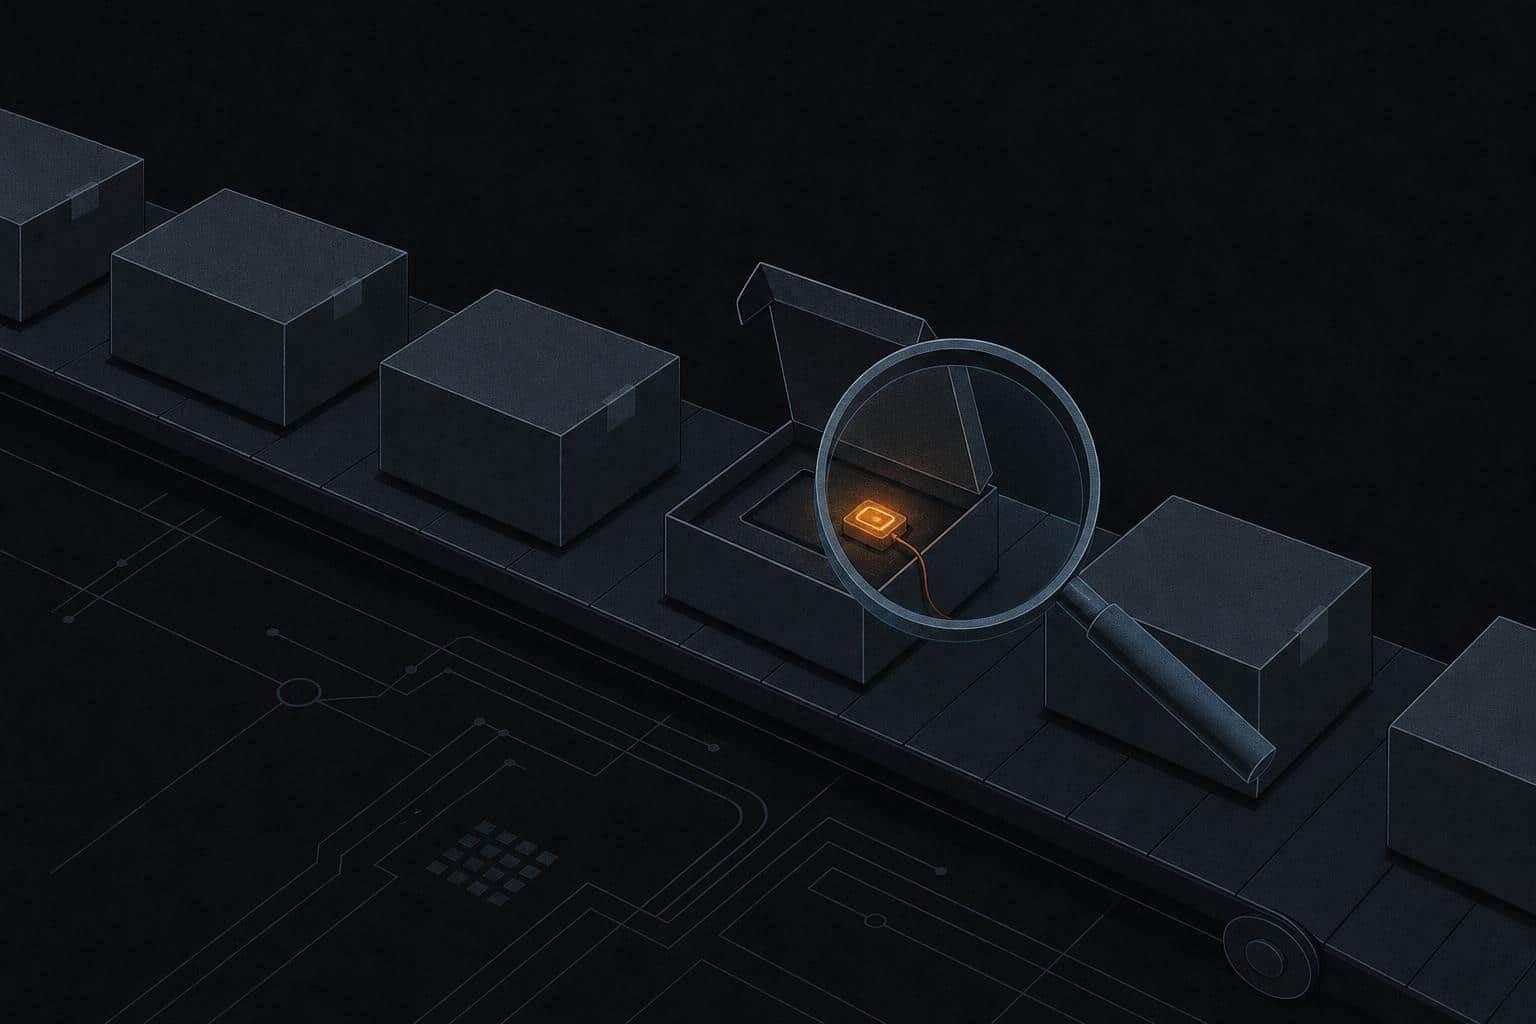
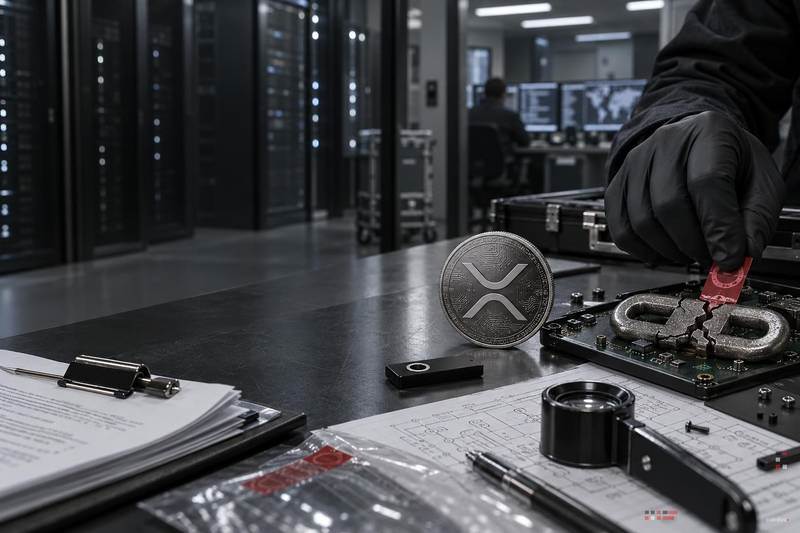
Ledger已证实,在一宗钱包盗窃案的调查过程中,在其一名客户拥有的设备内部发现了未授权的硬件植入物。这一发现引发了人们对硬件钱包物理供应链完整性以及用户对密封消费级设备所抱安全假设的尖锐质疑。
此次确认标志着主要硬件钱包制造商罕见地承认,一台经过修改的设备最终到达了终端用户手中。根据现有报道,尚无法确定该植入物是在设备离开供应链之前还是之后被引入的,且Ledger并未公开将该修改归因于分销过程中的特定行为者或阶段。
此次发现被定性为调查结果,而非大规模产品召回。目前的信息并未证实其他设备中存在此类植入物,也未确认制造或转售渠道存在系统性漏洞。用户需谨慎区分这一点:单台设备的确认发现本身并非更广泛攻击活动的证据,但也不能完全排除这种可能性。
未授权硬件植入物对设备完整性的影响
在此语境下,“硬件植入物”指未经制造商或所有者知情而添加到设备中的未授权物理组件。此类组件可能拦截签名操作、泄露助记词数据,或在固件或软件安全控制层之下引入可被利用的逻辑漏洞。由于它运行在硬件层面,标准的固件验证和软件侧审计可能无法检测到它。
此前进行的钱包盗窃调查将这一发现与财务损失直接联系起来,尽管在现有报道中,植入物与任何盗窃行为之间的因果关系尚未得到独立证实。调查人员在检查受损设备时发现了该组件;仅凭这一序列并不能证明植入物就是盗窃机制。
近年来,Ledger设备曾卷入多起高价值资产丢失事件。一笔总额达9290万美元的比特币、以太坊和TRON资金被盗事件与Ledger相关暴露有关;另一起事件中,CZ在一家Ledger转售商遭受8600万美元黑客攻击后呼吁隔离钱包。这些事件涉及软件层和转售渠道的漏洞;而硬件植入物则代表了一种不同且更具侵入性的攻击向量。
转售渠道的脆弱性已造成严重后果:一名与Ledger转售商事件相关的黑客随后将107万美元ETH转移至Tornado Cash,并将27万美元转入Binance,这表明供应链攻击造成的损失会迅速转化为链上洗钱活动。
Ledger用户应知悉的关键事项
Based on the available information, two points are supported and are directly relevant to users holding Ledger equipment assets:
First, Ledger confirmed that during a wallet theft investigation, an unauthorized hardware implant was found in a customer device. This confirmation is a verified situation; its scope, reasons and full technical details remain within the scope of ongoing's (ongoing) investigation.
Second, the existing information does not establish a broader user impact, and there is no public announcement confirming that other devices in circulation have similar modifications. Users who obtain equipment through unofficial resellers or second-hand markets face significantly higher risks than users who purchase directly from official channels. This concern existed long before this specific discovery.
For Bitcoin holders, the characteristics that make self-custody valuable-that is, the elimination of counterparty risk-depend entirely on the integrity of the signing device. Once the hardware layer is compromised, these safeguards will expire no matter how powerful the firmware or passphrase configuration is. Any user who doubts the origin of a device should treat it as a potentially infected device and move funds to a device with a verified, uninterrupted chain of custody before signing for further transactions.